Profet AI

Profet AI

When Trust Becomes an Attack Path: From PHP2Shell to AI Agent Security

Runtime vulnerabilities, compromised software supply chains, and AI-driven attacks are exposing security assumptions that enterprises can no longer afford to leave unchecked.

Manufacturing AI security depends on controlling what a compromised system or agent is allowed to do. Runtime patching, verifiable credential revocation, and separate authorization for operational changes help limit the impact of failures across connected systems.

For manufacturing IT teams, some of the hardest systems to secure are not the ones that frequently break down. They are the systems that have been running reliably for years, with little documentation and even less appetite for change.

Consider an internal web dashboard used to monitor equipment utilization or maintenance records. It may have been delivered by a systems integrator a decade ago, built on an older version of PHP, and subsequently connected to manufacturing execution systems (MES), enterprise resource planning (ERP) platforms, and production databases.

The original developer may no longer be involved. The system still works. Production teams depend on it, and nobody wants to risk disrupting operations by upgrading its underlying components without extensive testing.

Similar compromises accumulate in cloud and development environments.

Service accounts, API keys, and OAuth grants are created to keep CI/CD pipelines and integrations running. Release permissions may be temporarily expanded to address an urgent customer issue. Credentials that were intended for limited use remain active, while exceptions introduced for convenience are not always reviewed or rolled back.

Individually, these decisions may seem reasonable. Over time, they create layers of implicit trust that become increasingly difficult to audit.

The applications continue to function, but the permissions and dependencies underneath them tell a different story.

In late October 2026, several major security disclosures brought these risks into sharper focus.

On October 21, two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, were disclosed under the name PHP2Shell. Both carry CVSS v4.0 scores of 9.2. Researchers demonstrated unauthenticated remote code execution (RCE) in affected Apache mod_php environments, including attack paths that execute before application code runs. Other deployment models, including PHP-FPM, require separate assessment of their execution and request-lifecycle conditions.

That same day, LiteLLM disclosed that its official release pipeline had been compromised, allowing a malicious package to reach PyPI and container registries. Cloud platform Railway also reported unauthorized access to internal systems, with some customer environment variables potentially exposed.

The risks were not limited to faulty application code. They involved runtime behavior, software release processes, persistent credentials, and access to sensitive infrastructure.

Another development made the picture more concerning. On October 21, Microsoft published threat intelligence describing how Storm-0940 had used ARTEX, an agentic AI penetration-testing framework, to accelerate parts of its offensive operations. In multiple observed cases, attackers progressed from initial targeting to privileged cloud access in less than three hours.

Firewalls, vulnerability scanners, endpoint protection, and application security controls remain essential. What these incidents demonstrate is that organizations also need to examine the trust relationships those controls may not fully address.

A vulnerable runtime can be exploited before application code runs. A compromised release process can distribute malicious software through an official channel. A credential issued for legitimate work can become a route to broader access.

The question is no longer limited to whether one system can be compromised. It is also how far an attacker could move using the access that system already holds.

PHP2Shell: When the Runtime Is Compromised Before Application Code Executes

PHP2Shell deserves attention because the vulnerabilities affect assumptions that web application developers often take for granted.

Authentication, authorization, and input validation are commonly implemented in application code. Yet an HTTP request must first pass through the web server and PHP runtime before that code can execute.

A vulnerability in this earlier processing stage can create an attack path that application-level controls are not designed to prevent.
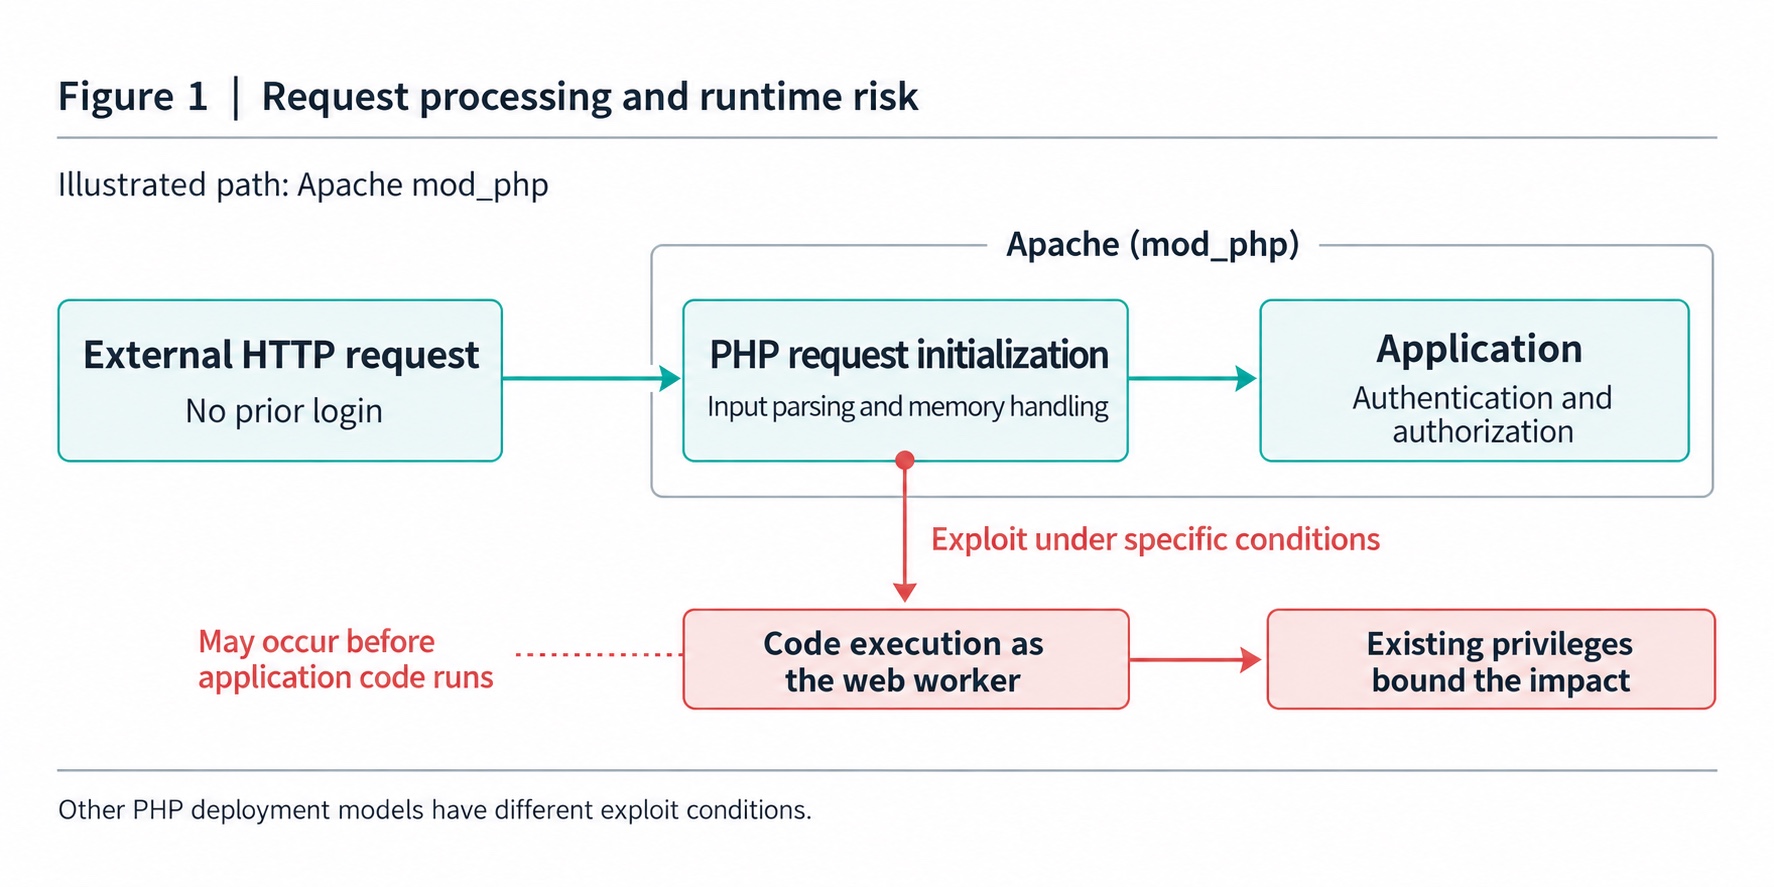
An external HTTP request enters PHP initialization inside Apache mod_php before application authentication; exploitation under specific conditions can grant code execution as the web worker.
Figure 1. An illustrated Apache mod_php request path. Other PHP deployment models have different exploitation conditions.

According to the PHP security team’s advisory, both vulnerabilities involve failures in how PHP handles memory and request state.

CVE-2026-109618: Memory corruption during out-of-memory handling

PHP uses error-handling mechanisms to terminate processing when memory allocation fails.

Under certain conditions, an allocation failure can interrupt request processing before internal state has been fully initialized. Subsequent cleanup operations may then treat invalid memory as valid, creating a memory-corruption vulnerability.

Specially crafted HTTP requests, including multipart form submissions, can trigger the affected processing paths.

The consequences can extend beyond a process crash or denial of service. Researchers demonstrated unauthenticated RCE against Apache mod_php, including exploitation before application code executes.

PHP-FPM is also considered potentially susceptible, but the PHP security team’s initial disclosure distinguished this from the demonstrated mod_php exploit. At that point, a complete PHP-FPM exploit for this vulnerability had not been publicly demonstrated.

The distinction matters. Different PHP execution models have different request lifecycles, error-handling behavior, and exploitation conditions. Organizations should assess their actual deployment configuration rather than assume that all installations have identical exposure.

See the official CVE-2026-109618 advisory.

CVE-2026-109619: Stale state across requests

The second vulnerability involves global state that persists within PHP worker processes.

Some internal state can retain references to memory belonging to a request after that memory has been released. Under particular error-handling and request-reuse conditions, subsequent processing may access the stale state before it is properly reinitialized.

This creates a use-after-free vulnerability that can potentially be exploited for remote code execution.

The underlying issue is not simply that an HTTP connection remains open. It concerns how worker processes retain and reuse internal state across requests or during interrupted processing.

The affected execution paths differ across PHP environments, and exploitation depends on the relevant runtime behavior.

See the official CVE-2026-109619 advisory.

Together, the vulnerabilities illustrate an important architectural risk: an application can contain sound authentication and validation logic while remaining vulnerable through the runtime that executes it.

If an attacker gains code execution with the web worker’s privileges, the potential damage depends partly on what that identity can access. A service account with unnecessary database permissions or access to adjacent applications can turn a runtime compromise into a broader incident.

Runtime patching and least-privilege access therefore need to be considered together.

The manufacturing problem: a critical patch with no easy maintenance window

PHP released fixes in versions 8.2.35, 8.3.36, 8.4.27, and 8.5.12.

For a modern application with automated testing and controlled deployments, upgrading may be relatively straightforward. For a decade-old manufacturing dashboard, the work can be more complicated.

The application may rely on an outdated PHP extension or database driver. It may run inside a virtual machine that has not been rebuilt for years, or within a container image that receives little maintenance. It may also be bundled with third-party equipment management software.

Updating the host operating system does not necessarily update the runtime inside a container. Redeploying an application does not guarantee that an embedded third-party dependency has been replaced.

An IT security team may see a critical CVSS score and demand immediate action. Operations may see a system tied to production and insist on a maintenance window, compatibility testing, and a rollback plan.

Neither concern can simply be ignored.

The right first step is to establish actual exposure:

  • Which PHP runtime and patch level are deployed, including any vendor backports?
  • Does the deployment use an affected execution model?
  • Can untrusted requests reach the vulnerable processing path?
  • What privileges does the web service hold, and which downstream systems can it access?
  • What would an upgrade or restart affect operationally?

Where an immediate upgrade is not feasible, organizations may need to narrow network access, remove unnecessary privileges, apply vendor-recommended configuration changes, strengthen request filtering, and increase monitoring.

These are temporary risk-reduction measures, not substitutes for a vendor-supported fix.

For unsupported PHP branches or older packaged applications, the organization should establish whether a vendor-maintained patch is available. The PHP security team has also published limited source backports for certain older versions, although these are not necessarily suitable for every environment.

If no supported fix is available, isolation and a controlled migration plan become increasingly important.

The challenge is not choosing between security and uptime. It is developing a patching process that accounts for both.

What PTC and Oracle Reveal About the Limits of Dependency Visibility

Following the PHP2Shell disclosure, major enterprise software vendors began publishing product-level impact assessments.

PTC established a dedicated PHP2Shell advisory page and reported that several core products, including ThingWorx, Windchill PLM, and FlexPLM, were not affected. For PTC Cloud, the company reported applying recommended protective measures and scanning environments to ensure relevant PHP executables and libraries were updated or removed.

Oracle published a security alert identifying affected versions across several products, including Oracle Communications Diameter Signaling Router and EAGLE Application Processor, as well as other Communications and infrastructure products.

These vendor responses give customers a starting point for assessing their own exposure.

However, the assessment of a standard product does not automatically describe every customized deployment in a customer’s environment.

Manufacturing software frequently passes through multiple layers of integration. A systems integrator may add a lightweight web service. An internal team may develop a reporting interface or connect the application to another database. A vendor-supplied package may include dependencies that are not obvious from its product name.

As a result, the application running on the factory floor may differ significantly from the standard configuration assessed by its original vendor.

This exposes a familiar limitation in enterprise asset management.

A configuration management database (CMDB) may identify a server’s hostname, IP address, application owner, and business function. Those records are useful, but they may not reveal:

  • The exact container image or build currently deployed.
  • The versions of libraries and runtimes contained in that artifact.
  • Dependencies introduced through customization or third-party integrations.
  • The service accounts, database connections, and API permissions associated with the deployment.
  • The upstream and downstream systems that could be affected by an emergency update.

A software bill of materials (SBOM) can improve visibility, but only when it reflects the software actually running.

An SBOM created during project acceptance and never updated offers limited value during an incident. The same applies to an asset inventory that is disconnected from CI/CD, container registries, runtime configurations, and identity management.

Ideally, organizations should be able to correlate a newly disclosed CVE with the deployed artifact, its dependencies, the environment in which it runs, and the access it has been granted.

Without that visibility, answering a question as basic as “Are we affected?” can require days of investigation across development teams, systems integrators, vendors, and operations.

For manufacturing environments with tightly controlled maintenance windows, that delay is more than an administrative inconvenience.

LiteLLM and Trivy: Removing a Secret from Git Is Not the Same as Revoking It

PHP2Shell illustrates the risks associated with the runtime. The LiteLLM incident exposes a different problem: the trust placed in official software distribution channels.

On October 21, 2026, LiteLLM’s release pipeline published a compromised version, litellm==1.107.0, to PyPI and container registries.

Users obtaining the affected package through an official distribution channel could therefore encounter malicious code without downloading anything from an obviously suspicious source.

One of the most consequential findings was that the official source release tag did not contain the malicious content. The compromise occurred in the process that produced and published the release artifacts.

Reviewing the legitimate source tag alone would not have established the integrity of what customers actually downloaded.

LiteLLM’s October 23 root-cause analysis reconstructs how the attacker reached that point.

1. A master key was exposed in May but never revoked

On May 27, a configuration file containing the master key to an internal LiteLLM Agent Platform deployment was accidentally committed to a public GitHub repository.

The exposed configuration was removed from the repository’s visible history, and the credentials were identified as requiring revocation.

The critical step, however, did not happen: the master key remained valid.

Deleting a secret from a repository does not invalidate copies that may already have been obtained. The credential must be revoked at the issuing service, and its downstream access must be assessed.

2. The key became a path to GitHub organization-level access

On October 10, an attacker used the still-valid master key to access the internal Agent Platform API.

That API returned a GitHub CLI OAuth token associated with a GitHub organization owner.

The token was not restricted to a narrowly scoped service identity. It carried extensive privileges across the organization’s repositories.

Armed with that access, the attacker created temporary CI workflows to exfiltrate additional secrets, including tokens belonging to other maintainers.

Some workflow execution records were subsequently deleted, although organization-level audit evidence remained available to investigators.

The original exposed key had become an entry point into multiple development and release systems.

3. The attacker redirected the release workflow to a malicious repository

On October 21, the attacker attempted to modify LiteLLM’s private release workflow so that it would build from a lookalike repository rather than the legitimate source.

Branch protection initially blocked the unauthorized change.

The attacker then used the organization owner’s credentials to override those protections and push the modified workflow.

This is an important distinction. A security control existed and worked as intended at first, but the broader permission model allowed a sufficiently privileged identity to bypass it.

4. Temporary approval changes made publication easier

Under normal circumstances, LiteLLM’s production release process required approval from a dedicated account associated with a physical device.

That requirement had been temporarily relaxed to support more frequent releases and bug-fix backports, allowing two authorized engineers to initiate and approve publication.

Because the attacker had already obtained multiple maintainer tokens, the modified approval process could be satisfied with stolen credentials.

The attacker used one token to initiate the compromised release and another to approve it.

The pipeline then signed and published the malicious artifacts through LiteLLM’s official infrastructure.

The sequence illustrates how multiple individually trusted mechanisms can be manipulated when an attacker gains enough control over the identities and workflows connecting them.

Trivy: When credential rotation leaves an opening

A related lesson emerged from the March 2026 supply-chain compromise involving Aqua Security’s Trivy ecosystem.

According to the project’s security advisory, the March attack followed an earlier incident disclosed at the beginning of the month.

Credential rotation had been performed, but the process was not atomic: not all credentials were invalidated simultaneously.

The advisory identifies a possible scenario in which a remaining valid token could have been used to obtain newly rotated secrets, allowing the attacker to retain access. That mechanism was presented as a potential explanation, rather than conclusively established.

On March 19, attackers used compromised credentials to publish a malicious Trivy release and redirect numerous GitHub Action version tags to malicious code. Additional compromised container images appeared on March 22.

The attacks affected tools that development teams commonly incorporate into automated security scanning and build workflows.

This creates a particularly difficult supply-chain scenario: a tool introduced to improve security can itself become a delivery mechanism for malicious code.

Both incidents point to several practical requirements.

Credential revocation must be verifiable. Removing a file or closing a ticket is not sufficient if the credential remains accepted by the issuing service.

Rotation must account for connected systems. Replacing one token while another compromised identity can still retrieve the replacement may leave the original access problem unresolved.

Release protections must withstand privileged-account compromise. High-risk workflow changes should require independent oversight, and temporary approval exceptions should have explicit expiration and restoration procedures.

Artifact provenance matters. A signed artifact can establish who or what signed it, but a valid signature alone does not prove that the build used the intended source or that the build process was uncompromised.

Organizations should validate the relationship between approved source revisions, build workflows, signed artifacts, and deployed versions. Immutable references, trusted build identities, audit records, and reproducibility checks can reduce the opportunity for substitution.

Official distribution remains valuable. The lesson is not to abandon trusted sources, but to verify the process by which software becomes an official release.
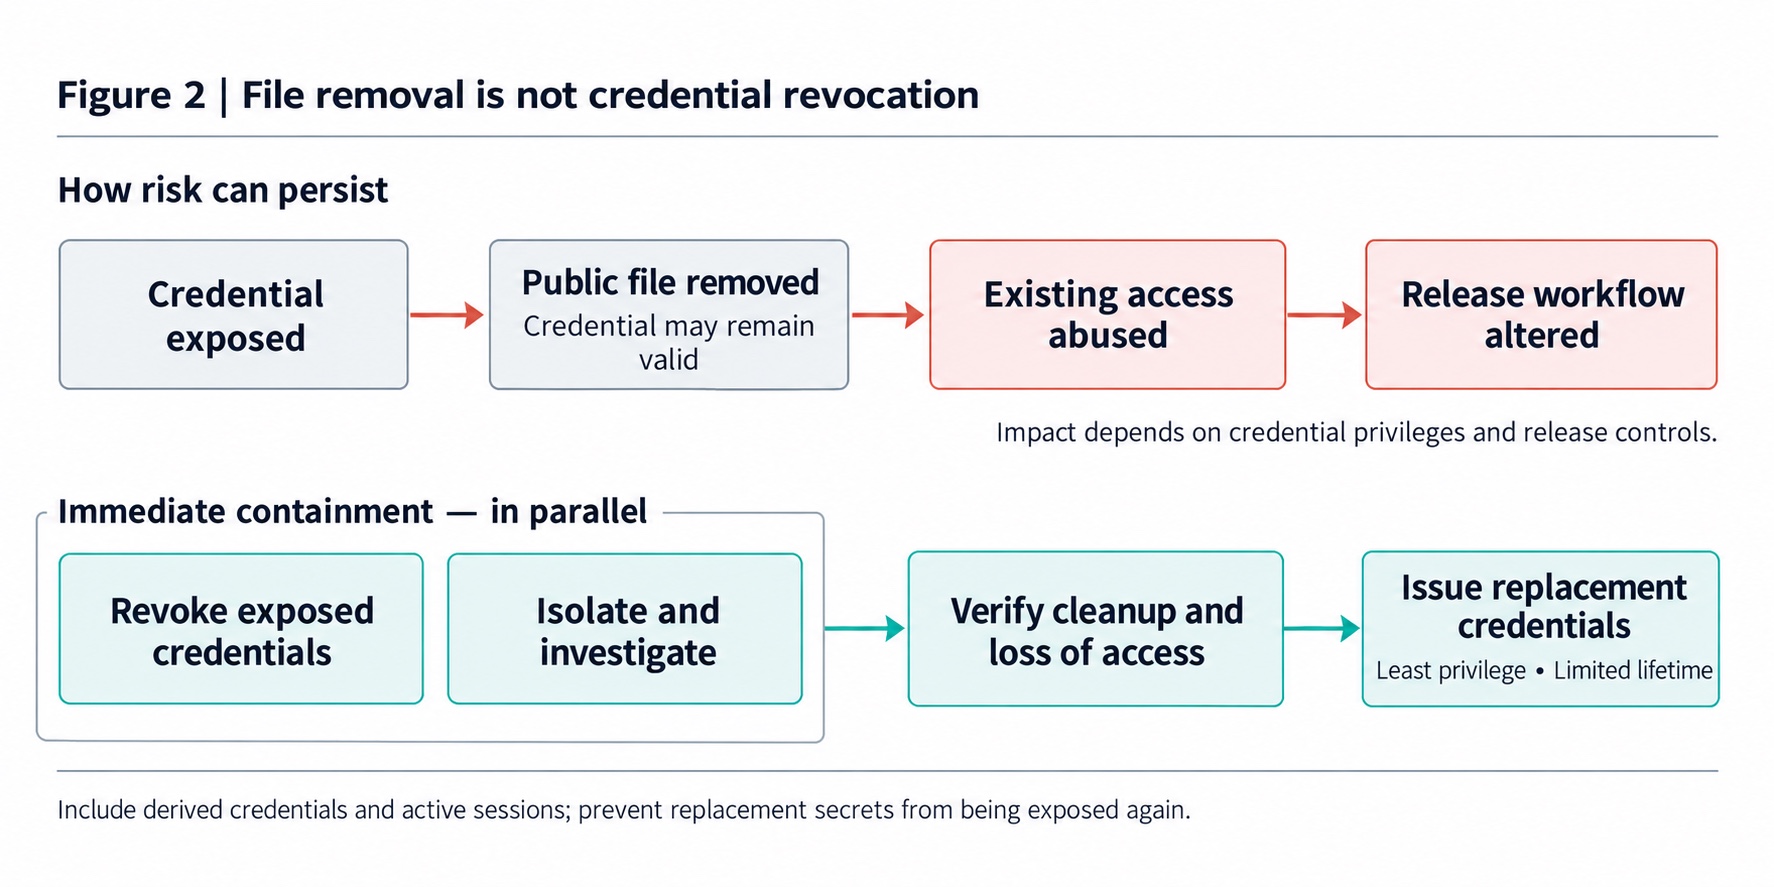
Removing a public file can leave an exposed credential valid. Revoke credentials and investigate in parallel, verify cleanup and loss of access, then issue least-privilege replacement credentials.
Figure 2. Removing a leaked file does not revoke its credentials. Containment and recovery must also address derived credentials and active sessions.

Railway: Encryption at Rest Does Not Eliminate Credential Exposure

The October 2026 Railway security incident drew attention to another widely used architectural pattern: secrets stored as environment variables and accessed by automated services.

Cloud-native applications routinely rely on API keys, service accounts, and other non-human identities (NHIs) to communicate with databases, infrastructure services, and external providers.

These credentials enable automation. They also create attractive targets when the identities or systems permitted to use them are compromised.

According to Railway’s October 22 preliminary incident report, the attack began on October 20 and continued through October 22, when Railway confirmed that the attacker no longer had access to its internal systems.

The investigation confirmed unauthorized access to a subset of those systems. Railway also reported that the attacker accessed encrypted customer environment variables and decrypted stored secrets for a subset of workspaces.

The company estimated that no more than 1.85% of workspaces had potentially compromised environment variables.

That figure does not mean every secret within those workspaces was accessed or exfiltrated. Railway also stated that it could not determine exactly which variables had been decrypted.

The complete intrusion mechanism had not been disclosed in the preliminary report. In particular, the report does not establish container escape as the confirmed entry point.

What it does establish is the operational importance of protecting the infrastructure identities and services involved in handling secrets.

Encryption at rest is an essential security measure, but applications and infrastructure services must eventually decrypt the secrets they are authorized to use.

If an attacker compromises an identity or system with legitimate decryption privileges, encrypted storage alone cannot prevent misuse of that authorized access path.

Railway’s investigation indicated that the attacker was particularly interested in high-value AI provider and platform API keys.

The incident also highlights an important distinction in credential recovery.

Revoke exposed credentials promptly; reissue them into a trusted environment

Incident response often treats credential rotation as a single step, but two separate actions are involved.

The first is containment: revoke or disable credentials that are known or reasonably suspected to have been exposed.

The second is recovery: issue replacement credentials and deploy them only after the relevant systems and access paths have been secured.

Railway reported notifying upstream providers so potentially affected credentials could be revoked. It also delayed asking customers to deploy replacement credentials until the immediate intrusion had been contained, reducing the chance that newly issued secrets would be compromised again.

For manufacturing operations, the same distinction applies.

An organization may be unable to shut down every connected system immediately. It still needs a clear understanding of which credentials and access paths require urgent containment, which services must remain available, and how recovery should be sequenced.

The objective is not simply to generate new keys. It is to prevent the attacker from retaining access while keeping critical operations under control.

Agentic AI Is Compressing the Time Available to Defenders

Credential abuse and supply-chain compromise are not new attack techniques. What is changing is the speed and scale at which attackers can combine them.

Microsoft’s October 21 threat intelligence report described how Storm-0940, a state-aligned threat actor, used ARTEX, an agentic AI penetration-testing framework, to automate elements of its offensive operations.

Microsoft observed activity involving automated reconnaissance, password spraying, OAuth application abuse, and follow-on actions in cloud environments.

In multiple instances, the time between initial targeting and privileged cloud access was less than three hours.

That finding should not be interpreted as a universal three-hour compromise window. Nor does it mean every automated attempt succeeded.

Microsoft also documented unsuccessful activity, including a large password-spraying campaign in which its telemetry recorded more than 151,000 failed sign-in attempts without observing successful authentication.

The significance of the findings is not that AI-assisted attacks consistently compromise organizations within hours. It is that certain successful intrusions progressed at a pace that can outstrip conventional investigation and response workflows.

During activity associated with the ConnectWise supply-chain compromise, Microsoft observed attackers abusing credentials associated with applications that customers had previously authorized.

That existing authorization was significant. The attacker could attempt to access downstream cloud environments through application identities without requiring a new interactive user sign-in.

Some observed activity then progressed to Microsoft Graph operations, including reconnaissance and changes involving application credentials and permissions.

For defenders, this changes the operating assumptions.

A conventional response process might involve an alert, analyst review, escalation to the application owner, business-impact assessment, and an approved containment or maintenance action.

That process may take hours or days, particularly when production continuity is involved.

An AI-assisted attacker can attempt multiple paths in parallel while moving through already authorized services.

Organizations therefore cannot depend entirely on discovering excessive privileges during an incident. They need to reduce unnecessary access beforehand, monitor non-human identities, and establish containment procedures that can act quickly without introducing unacceptable operational risk.

This is a different problem from deploying AI agents inside an enterprise. ARTEX was an offensive framework used by a threat actor.

The connection is architectural: the more actions an automated system can perform with existing privileges, the more important the boundaries around those privileges become.

AI Agents in Enterprise Operations: Keep Analytical Access Separate from Execution Authority

As enterprises introduce AI agents into operational workflows, identity and access management take on new significance.

An agent may retrieve documents, query databases, invoke APIs, and coordinate actions through tool-calling frameworks or the Model Context Protocol (MCP).

These capabilities make agents useful. They also mean that a poorly scoped identity can give an otherwise limited assistant far more authority than its intended role requires.

Consider an equipment troubleshooting agent in a manufacturing plant.

An engineer wants the agent to review maintenance manuals, query sensor readings, retrieve historical fault records, and recommend possible causes of an equipment anomaly.

The intended workflow is analytical. The agent needs access to information, not the authority to change equipment settings.

During integration, however, the team may reuse an existing service account because it already connects to the relevant systems.

That account might also have permission to update maintenance records, create work orders, modify production schedules, or invoke commands through another operational application.

The agent has now inherited privileges beyond its original purpose.

If the agent encounters malicious instructions embedded in retrieved documents, tool responses, or other untrusted content, an indirect prompt injection attack may cause it to misuse otherwise legitimate tools.

The resulting impact depends on the permissions granted to the agent and the controls enforced by the connected systems.

Likewise, a compromised dependency or tool integration could introduce additional risk if it operates with excessive privileges.

These are potential attack scenarios, not evidence that the incidents discussed earlier involved compromised manufacturing agents.

The concern is that legitimate tool access can be misused when authorization is broader than necessary.

A prompt instructing an agent not to modify production data is not a security control. Enforceable boundaries must exist in the identity, API, workflow, and infrastructure layers.

Three design principles are particularly important.

1. Separate read access from operational changes

An agent used for diagnosis should have read-only access wherever possible, enforced through the connected systems rather than described only in its instructions.

Even read-only access needs controls.

An agent that can retrieve confidential information and send it to an external destination may still create a data-exfiltration risk. Data access and outbound communication should both be restricted according to the task.

Actions that change operational state require stricter treatment.

Changing equipment parameters, altering production plans, or initiating procurement should pass through explicit authorization checks. Depending on the operation’s criticality, that may include human approval.

Approvals should be meaningful. Reviewers need to see the proposed action, the relevant equipment or records, the expected changes, and the potential consequences.

A generic approval button without sufficient context provides little protection.

2. Scope machine identities to the task and duration

Agents should not automatically inherit broad administrative permissions from the systems they connect to.

Where supported, organizations should use dedicated identities, narrowly scoped authorization, and short-lived credentials.

The objective is to grant an agent only the access required for a specific task, for as long as that task requires it.

Short-lived credentials are not always practical in older operational environments. Some industrial applications were not designed for modern identity protocols, dynamic credential issuance, or frequent reauthentication.

In those cases, the goal remains the same, but the architecture may need to enforce controls through an intermediary rather than directly on the legacy system.

Regardless of credential lifetime, the organization should be able to identify who or what initiated an action, which permissions were used, and whether access remains necessary.

3. Put a controlled interface between agents and legacy OT systems

Manufacturing environments cannot assume that every existing machine or control system supports modern security mechanisms.

For older equipment, a controlled gateway or intermediary service can enforce policies between an AI agent and the production network.

For example, an agent may be permitted to retrieve equipment status from an approved interface, while changes to operating parameters require an additional authorization step.

Controls can also restrict which equipment is accessible, which commands are permitted, how frequently requests may be made, and whether outbound connections are allowed.

Network segmentation between enterprise IT and operational technology (OT) remains important. A compromised business application or agent should not have unrestricted access to production systems.

These boundaries help ensure that an analytical assistant does not inadvertently become an operational control channel.
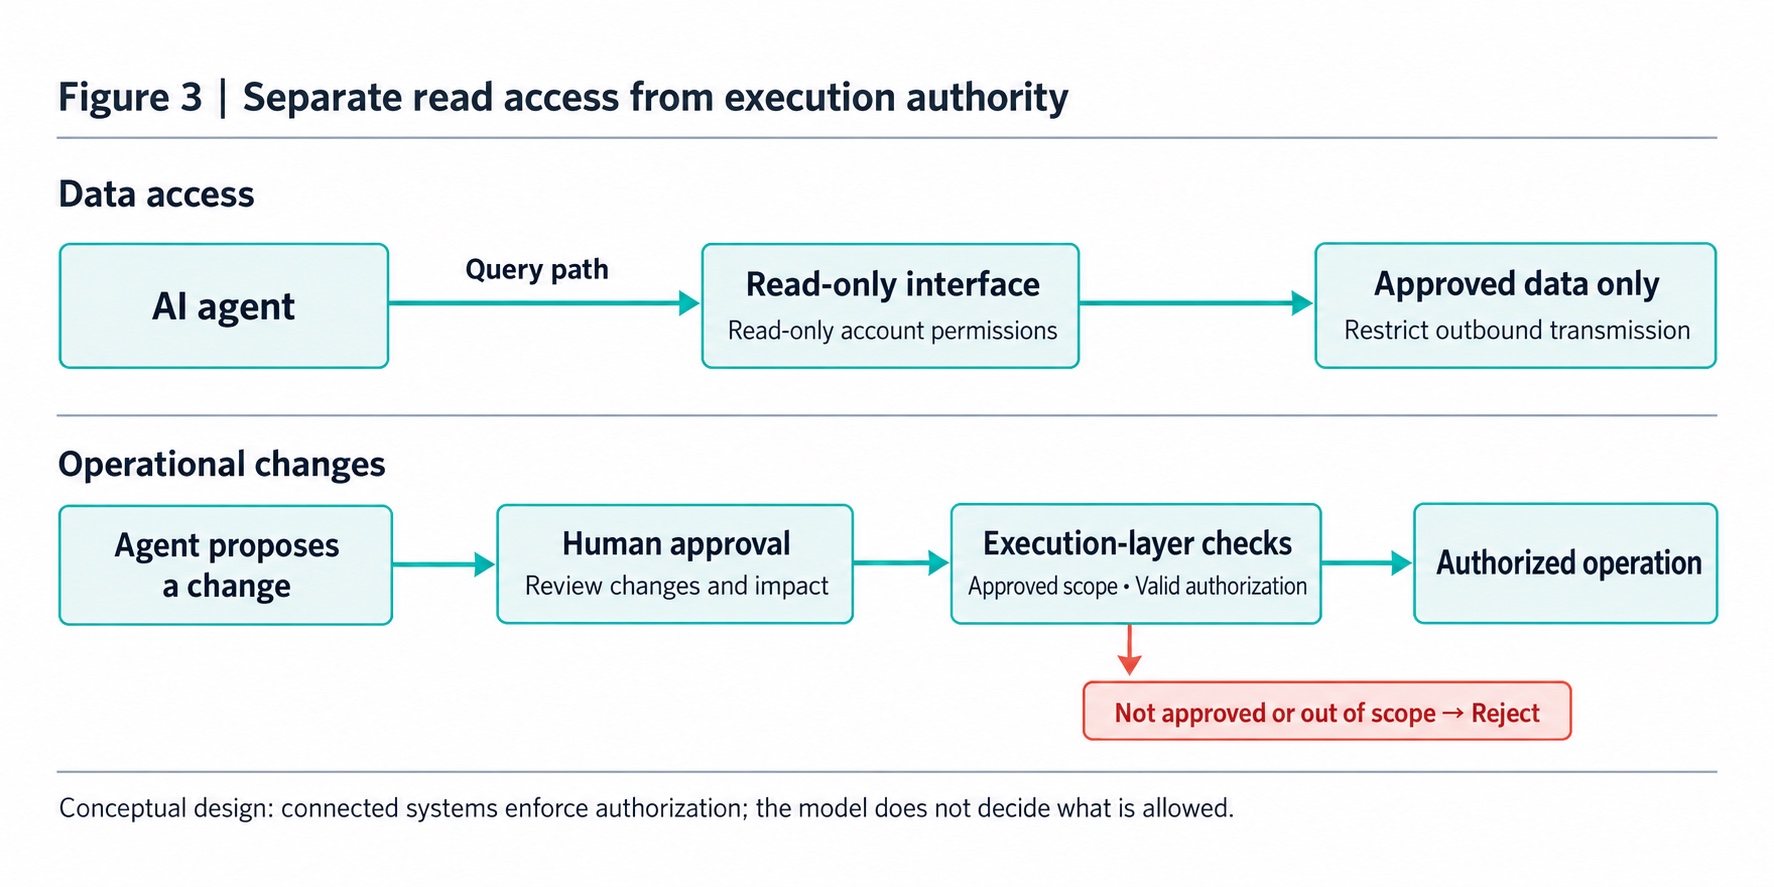
AI agents query approved data through read-only access. Operational changes pass through human approval and execution-layer authorization checks; requests outside the approved scope are rejected.
Figure 3. A conceptual separation of analytical access and operational authority. Read-only access still requires data-scope and outbound-transmission controls.

At Profet AI, the same principles inform our approach to Domain Twin™, which brings machine learning and agentic AI into enterprise manufacturing workflows.

The objective is not to assume that models will always interpret information correctly or resist malicious input. It is to place agent capabilities within a governable operating environment, with defined access permissions, appropriate human oversight, and auditable activity.

As AI moves beyond analysis and begins participating in operational decisions, the separation between recommendations and authorized execution becomes an essential part of enterprise deployment.

After Pandora’s Box Opens: Making Security a Continuous Engineering Practice

Taken together, these incidents expose limitations in security assumptions that organizations have long relied upon.

An unchanged application may still be exposed through its underlying runtime.

A package obtained from an official distribution channel may still be compromised if the build or release process has been manipulated.

Encrypted secrets may remain vulnerable when an attacker gains access to the identities authorized to decrypt them.

And AI-assisted attacks can accelerate the abuse of existing credentials and permissions, leaving defenders less time to investigate and respond.

None of this makes conventional security practices obsolete.

Patching, vulnerability scanning, network controls, identity management, and incident response remain fundamental. The problem is treating any one of them as a complete defense.

Patching is essential, but patching alone is not a security strategy.

The need for continuous vulnerability management extends well beyond PHP.

Java-based systems, including applications built on Apache Tomcat, Node.js services, and other widely deployed components all require ongoing dependency monitoring and exposure assessment.

For manufacturing organizations, the process must also account for maintenance windows, validation requirements, and operational continuity.

That means connecting several activities that are too often managed separately:

  1. Continuous vulnerability intelligence: Monitor new CVEs and vendor advisories for components relevant to the environment.
  2. Actual exposure assessment: Determine which deployed versions, configurations, and access paths are affected, rather than treating every published CVE as an equally urgent patch.
  3. Risk-based remediation planning: Prioritize action based on exploitability, exposure, privilege, business criticality, and available mitigations.
  4. Controlled deployment and validation: Test security updates against system dependencies, document changes, and verify that remediation is effective.
  5. Ongoing visibility: Keep component inventories, deployment records, credentials, and vendor dependencies current as systems change.

These activities need to form a repeatable operating process, not an emergency exercise reconstructed each time a critical vulnerability appears.

How Profet AI Is Putting This into Practice

In response to recent major security advisories, Profet AI has conducted product-level component reviews and vulnerability scanning across relevant software components and container images.

The team is using those findings to assess potential impact and coordinate security updates with compatibility testing.

A further change is taking place in day-to-day monitoring.

Profet AI has introduced an internal security monitoring agent that checks CVE updates daily and helps filter advisories according to relevant software components and severity.

The purpose is not to hand security decisions entirely to AI. It is to reduce the manual effort involved in sorting through large volumes of vulnerability disclosures so that engineering and security teams can focus on confirming exposure, assessing impact, and validating remediation.

Alongside its existing product release cycle, Profet AI is developing a more structured process for delivering critical security fixes and communicating the relevant CVEs, affected product versions, and remediation status.

The aim is to give customers the information they need to coordinate updates with their operational and compatibility requirements.

This responsibility is shared.

Software providers must maintain visibility into their dependencies, protect the integrity of their release processes, communicate security issues transparently, and deliver appropriate fixes.

Enterprise customers must assess their deployed environments, manage network access and operational identities, and plan updates within their business and production constraints.

Neither side has complete visibility into the other’s environment. Effective security depends on maintaining that connection.

The same thinking applies as ML and agentic AI become more deeply embedded in manufacturing engineering and operational workflows.

Data access, tool invocation, approvals, and auditability need to be designed around clear boundaries, not left to assumptions about how an AI model will behave.

Major vulnerabilities may dominate the headlines for a few days. The underlying environment, however, changes continuously.

New dependencies are introduced. API integrations are added. Service accounts gain permissions. Software is upgraded, replaced, or quietly left running long after its original maintainers have moved on.

There will always be another vulnerability to investigate. The more durable question is whether the organization knows enough about its own systems to respond effectively.

That is a more meaningful measure of security resilience than whether an organization can claim it has never experienced an incident.

Resilience means being able to identify exposure early, understand its operational consequences, contain the impact, and recover without losing control of the systems the business depends on.

As enterprises put AI to work, maintaining that control will matter as much as the capabilities they choose to deploy.

Related reading

Sources and security guidance

When Trust Becomes an Attack Path: From PHP2Shell to AI Agent Security Read More »
From Digital Twin to Domain Twin™: Closing the Industrial AI Loop

INDUSTRIAL AI · TECHNICAL ARCHITECTURE

A technical architecture for connecting NVIDIA-enabled physical-world intelligence with manufacturer-specific expertise, Machine Learning, Agentic AI, governance and action

Industrial digital twins model physical state and possible outcomes. Profet AI Domain Twin™ adds manufacturing knowledge, model evidence, permissions and workflows so teams can turn that evidence into governed action and reusable operating expertise.

ARCHITECTURE PREMISE

In this architecture, the industrial digital twin provides a computable model of the physical operating environment. Domain Twin™ makes the manufacturer-specific knowledge, model evidence, decision rights and governance around that environment machine-operable.

Manufacturers have spent years building digital representations of factories, production lines, machines and products. That work is now converging with Physical AI. NVIDIA positions industrial digital twins across design, simulation, operation and optimization. NVIDIA Omniverse™ libraries and OpenUSD provide interoperable 3D data, physics, sensor simulation and validation capabilities for building simulation-ready environments used in Physical AI development.

For factory engineering, the result is a physical environment that is increasingly computable and testable. Teams can examine what is happening on a line, test how layout changes affect material flow, validate robot behavior, and evaluate throughput, energy use and other operating constraints before touching the live system. For robots, autonomous systems and AI agents that interact with the physical environment, these virtual environments also provide a controlled place to test and validate behavior before deployment. The harder engineering problem begins when physical evidence has to become an enterprise decision. The response to the same abnormal signal may depend on the active recipe revision, the current lot, maintenance history, the latest SOP, a model’s validated operating window, an engineer’s judgment and whether the system or agent is authorized to act.

Domain Twin™ is designed for that enterprise decision state. It turns accumulated manufacturing expertise, model evidence, decision logic, permissions and workflows into machine-usable operating context. Physical-state evidence can then be interpreted against the manufacturer’s own rules, responsibilities and operating history rather than treated as an isolated signal or model output.

Digital Twin models physical state. Domain Twin™ carries enterprise decision context.

The two twins encode different forms of state. In this reference architecture, the digital twin represents physical state, behavior and constraints; Domain Twin™ carries the enterprise expertise and decision logic applied around them. One provides evidence about what is happening, or what may happen under a given physical condition. The other provides the context for deciding what this manufacturer should do next, based on its knowledge, models, policies and responsibilities.

Comparison pointIndustrial Digital Twin / Physical-World IntelligenceDomain Twin™ / Enterprise Domain Intelligence
What it modelsPhysical state, geometry, constraints and behavior.Enterprise knowledge, engineering experience, AI / AutoML models, procedures and decision logic.
Typical inputsEquipment state, sensor data, process conditions, simulated outcomes and physical constraints.Engineer know-how, SOPs, historical cases, quality data, model outputs, policy, permissions and workflow context.
Questions it helps answerWhat is happening? What could happen if the layout, process or robot behavior changes? How would throughput, energy use or material flow respond?Given our knowledge, policies and experience, what should we check, decide or authorize next?
Contribution to the loopA testable representation of the physical world.An operational representation of how the organization understands, decides and acts.

Table 1. Two complementary forms of context inside the same industrial AI loop. This is an architectural split, not a limit on digital-twin functionality; NVIDIA industrial digital twins also extend into live operations and optimization.

What Domain Twin™ adds: enterprise expertise as an operating model

Manufacturing expertise is distributed by nature. It lives with experienced engineers, in SOPs, troubleshooting records, process parameters, maintenance history, quality reports and engineering documents. It also lives in AI and machine-learning models built for specific products, equipment families and operating windows.

What is hardest to replicate is not the documents themselves, but the reasoning that connects them. When an abnormal condition occurs, what should be checked first? Which historical cases are genuinely comparable? When is a model output strong enough to support a recommendation? When must a human approve the next step? Which engineer, system or AI agent is authorized to carry it out?

Within this architecture, Domain Twin™ functions as the enterprise AI brain for manufacturing: the layer that makes operating knowledge, model evidence, decision rights and workflows explicit enough for AI to use and for the enterprise to govern. People, Process, Knowledge and Data form the context around five functions: understand context and intent, reason across multiple sources, decide within defined options and policy, govern safety and compliance, and translate an approved decision into action. The knowledge layer can include engineering know-how, SOPs, historical cases, AI and AutoML models, quality evidence and decision logic.

Within Domain Twin™, Machine Learning and Agentic AI are complementary capabilities. AutoML provides the Machine Learning capability for structured manufacturing data, turning it into prediction, anomaly-detection and optimization models whose outputs can serve as decision evidence. AI Studio provides the Agentic AI capability: orchestrating agents across the Model Hub, Knowledge / RAG and catalogs, Tools / MCP integrations, Memory, Guardrails, ACL / ABAC and Audit. Agents can retrieve approved knowledge, invoke analytical tools or AutoML models, compare historical cases and carry a decision into a governed workflow. To make that context reusable, the system also has to preserve provenance, applicability, authority and action scope.

Retrieval alone is insufficient. A RAG system may return the right SOP, but it does not by itself establish whether that revision is valid for the active recipe, whether a model applies to the current lot, or whether the caller is authorized to act. Domain Twin™ keeps those relationships attached to the decision state.

Reference architecture: from physical state to governed action

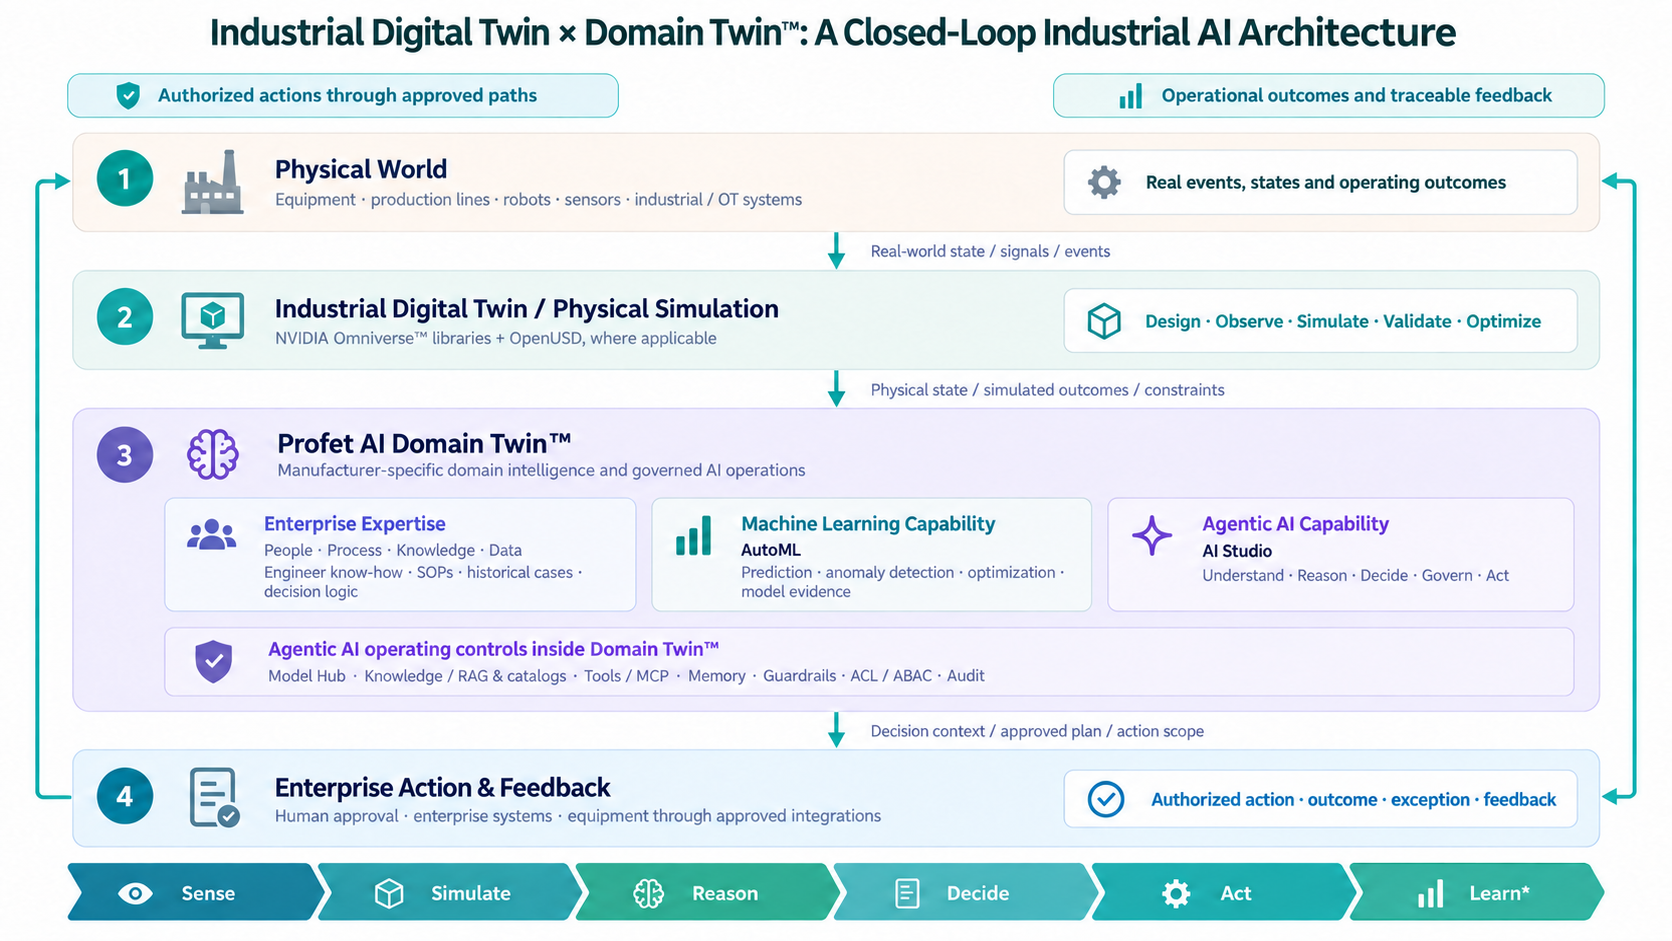
Closed-loop architecture linking the physical factory, industrial digital twin, Domain Twin manufacturing intelligence, and authorized enterprise action with feedback.

Figure 1. Complementary architecture: physical-world intelligence and Profet AI Domain Twin™ exchange state, constraints, decisions and operational feedback inside a governed closed loop. Domain Twin™ is the product layer; AutoML and AI Studio provide its Machine Learning and Agentic AI capabilities.

LayerTechnical roleWhat it contributes
1 · Physical worldEquipment, production lines, robots, sensors and industrial / OT systemsGenerate real-world events, telemetry, operating state and execution results.
2 · Industrial digital twin / Physical simulationOpenUSD scene data and NVIDIA Omniverse capabilities, where applicableRepresent, simulate, validate and optimize the physical environment, behavior and constraints.
3 · Profet AI Domain Twin™Enterprise expertise (People, Process, Knowledge, Data); Machine Learning capability (AutoML); Agentic AI capability (AI Studio) with Model Hub, Knowledge / RAG, Tools / MCP, Memory, Guardrails, ACL / ABAC and AuditTurn manufacturer-specific expertise into machine-usable decision context; combine model evidence and agentic workflows; govern reasoning, authorization and action.
4 · Enterprise action & feedbackHuman approval, enterprise-system write-back and equipment response through approved pathsExecute only within authorized scope; retain results, exceptions and feedback for audit and governed improvement.

Table 2. Four interacting layers connect physical-state evidence with enterprise decision logic and governed agent operation.

The most important engineering boundary sits between physical state and enterprise decision state. Asset identity, plant and line hierarchy, recipe revision, lot identity and timestamps have to align before an agent combines physical signals with enterprise knowledge. Model outputs need version and applicability context. Authorization must remain separate from reasoning: permission to inspect an event is not permission to modify a system. Treating this boundary as an explicit interface, rather than hiding it inside an LLM prompt, is what makes the architecture testable and governable.

From simulation to decision to action: a semiconductor equipment abnormality

Consider an equipment abnormality in a semiconductor factory. Equipment telemetry shows behavior drifting outside the expected operating range. A digital twin or another physical-world data and simulation layer can describe the equipment, surrounding environment and current state, and, where simulation is available, expose relevant physical constraints or the likely effect of a proposed change.

Diagnosis rarely depends on sensor data alone. An experienced engineer may correlate the alarm with maintenance history, process conditions, the active recipe and key parameters, recent lot context, prior failure cases, equipment documentation, quality data, the current SOP and analytical or AutoML model outputs. Within Domain Twin™, the Agentic AI capability can bring those sources into the same decision context, invoke approved models and tools, and compare the current event with historical cases rather than treating each source in isolation.

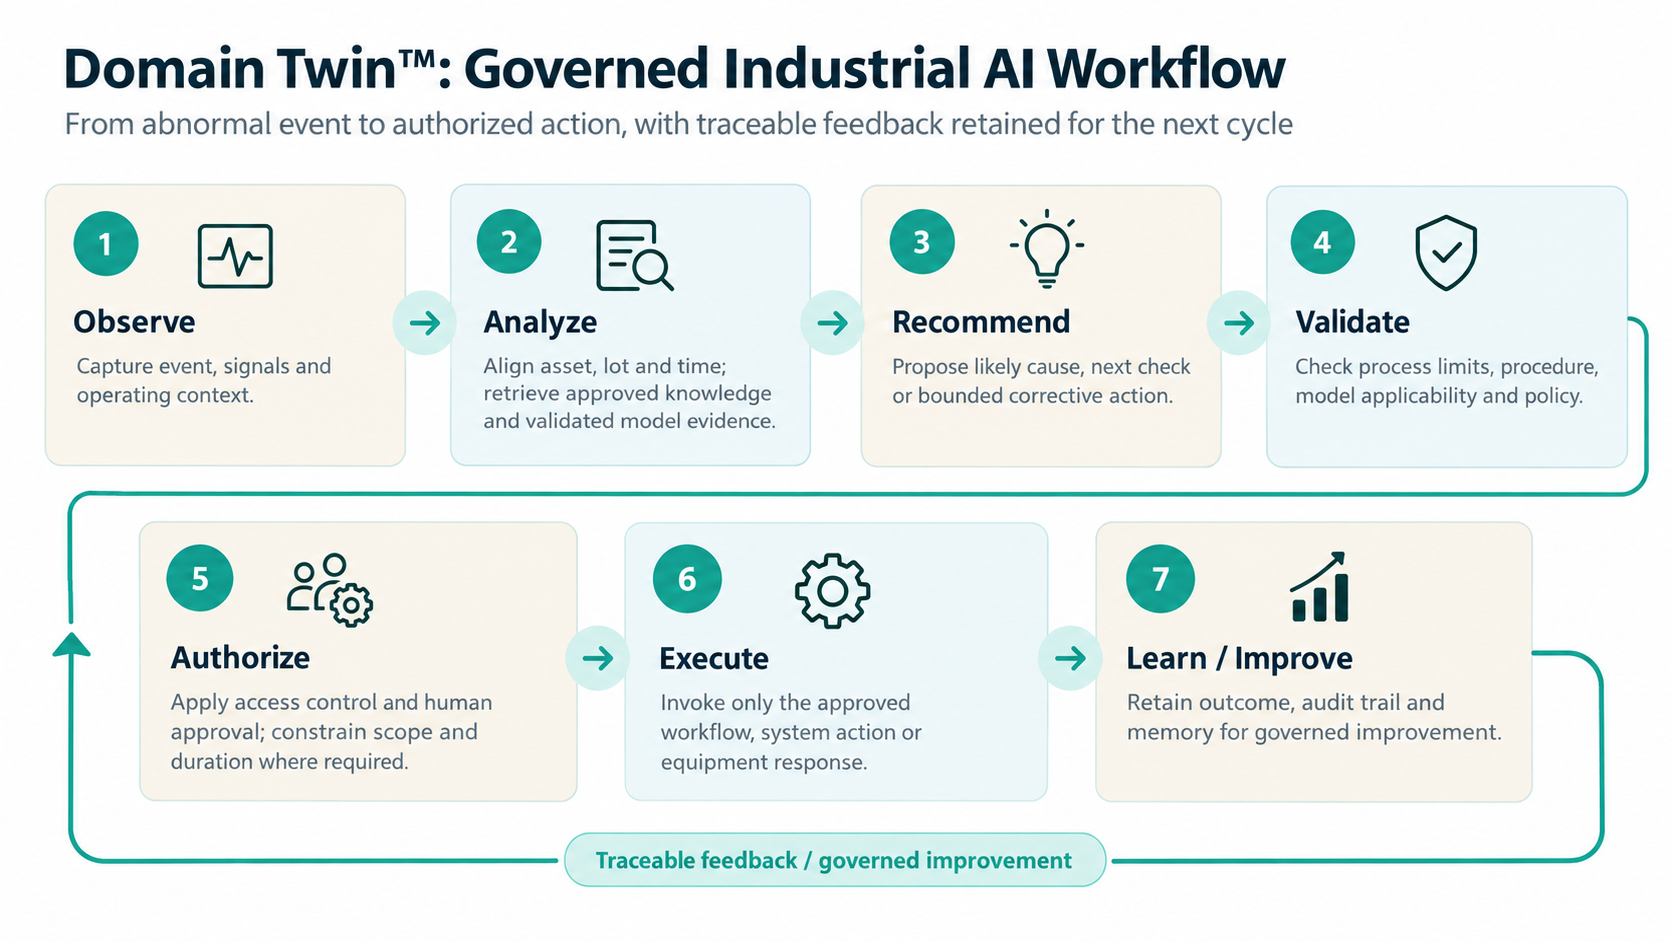
At that point, the agent enters a stateful enterprise workflow. It observes the event, analyzes the relevant evidence, recommends a bounded next step, validates it against operating rules and model limits, routes it through the required authorization, and only then invokes the approved action. The outcome returns to the system as traceable feedback for the next decision cycle. The result is a governed operational workflow in which AI participates under explicit enterprise controls.

Governed industrial AI workflow: observe, analyze, recommend, validate, authorize, execute, then learn and improve through traceable feedback.

Figure 2. Domain Twin™ governed industrial AI workflow: an abnormal event moves from observation and analysis through recommendation, validation, authorization and execution, with results retained as traceable feedback.

StepEngineering behavior
ObserveCapture the abnormal event, equipment signals, telemetry and operating context.
AnalyzeCorrelate data, historical cases, SOPs, engineering knowledge and analytical / AutoML evidence.
RecommendPropose likely causes, the next inspection or a bounded corrective action with supporting evidence.
ValidateCross-check the recommendation against operating limits, approved procedures, model applicability and enterprise policy.
AuthorizeApply RBAC / ABAC and Human-in-the-Loop controls. Where used, issue time-bounded authorization scoped to the action and duration.
ExecuteInvoke only the approved workflow, enterprise-system action or equipment response within the authorized scope.
LearnRecord outcome, audit trail and memory. Feed the result into governed knowledge, model or workflow improvement.

Table 3. Engineering behavior behind a governed abnormal-event workflow.

Governance belongs in the runtime architecture

Once an agent can use enterprise tools, write back to systems or affect equipment, governance becomes runtime behavior. RBAC or ABAC can determine whether the agent may access a particular model, knowledge source or tool. Human-in-the-Loop controls can require a qualified engineer to approve high-impact actions. Where used, a time-bounded authorization token can constrain both permission scope and duration. Every consequential step should leave enough evidence to reconstruct what the agent saw, which sources and models it used, who approved the action and what happened afterward.

Learning belongs inside the same control model. Operational outcomes can be retained as feedback, memory and new enterprise knowledge for the next decision cycle. Model retraining, knowledge changes and workflow updates should still pass through their own validation, versioning and governance before they return to production.

How this architecture aligns with NVIDIA Physical AI

NVIDIA describes a three-computer solution for Physical AI spanning training, simulation and real-time inference and control. DGX systems support training; Omniverse and Cosmos on RTX PRO Servers support simulation; Jetson AGX systems support real-time inference and control. NVIDIA’s industrial digital twin portfolio also extends into operation and optimization. The Factory Operations Blueprint (FOX) is a reference design for building autonomous factory-manager agents that reason across live factory data and coordinate specialized agents and machines.

As NVIDIA capabilities extend into live factory operations, manufacturer-specific domain context becomes a core architecture requirement. Orchestration can coordinate agents and machines, but it cannot know a manufacturer’s recipe authority, valid SOP revision, model operating window, escalation path or plant-specific exception unless those states are represented explicitly. Domain Twin™ is designed to carry that context.

Physical AI stageNVIDIA roleDomain Twin™ contribution
Training / model developmentTrain and improve AI capabilities with accelerated computing and data.Bring validated model outputs into the enterprise knowledge and decision context.
Simulation / digital twinRepresent, test and optimize physical environments, behavior and constraints before deployment.Use physical state, simulated outcomes and constraints as evidence in enterprise reasoning and decision workflows.
Inference / factory operationsRun AI close to physical systems and coordinate operational AI patterns, including factory-agent architectures.Apply manufacturer-specific knowledge, decision logic, permissions, approval conditions and governed workflows around what happens next.

Table 4. NVIDIA Physical AI and Domain Twin™ address different, complementary parts of the industrial AI lifecycle.

A closed loop depends on bidirectional context and constraints

The loop is bidirectional. Physical-world systems and digital twins can provide real-time state, simulated outcomes and physical constraints to Domain Twin™ and its agents. Domain Twin™ can return enterprise goals, engineering logic, decision rules, security policy and human-approval requirements to planning and execution. Once a decision is validated and authorized, the agent can translate it into an enterprise-system action or approved equipment response. The result then returns as feedback, memory and enterprise knowledge for the next cycle.

Exchange directionTypical content
Physical world / Digital Twin → Domain Twin™Equipment state, telemetry, simulated outcomes, physical constraints and event identity
Domain Twin™ → planning / agent workflowEnterprise goals, engineering logic, SOPs, model evidence, security policy and human-approval requirements
Agent workflow → enterprise / equipmentRecommended action, evidence summary, authorized parameters and target tool / system
Outcome → Domain Twin™System response, exceptions, engineer feedback and operating result retained as feedback, memory and enterprise knowledge

Table 5. The operating loop closes only when context, constraints and outcomes can move in both directions.

Where Domain Twin™ fits in the NVIDIA industrial AI ecosystem

NVIDIA’s industrial AI foundation now spans digital twins, Physical AI and factory-level agent orchestration. What remains manufacturer-specific is the operating context around that foundation: recipe ownership, SOP validity, trusted historical cases, model applicability, approval matrices and the differences between products, lines, plants and regions. The more capable the horizontal foundation becomes, the more important it is to formalize this domain layer, because models, agents and physical systems need to share the same operating semantics and decision rights.

NVIDIA’s Foxconn case study illustrates the physical side of portability: standardized OpenUSD-based digital-twin assets are used to migrate and duplicate production-line layouts across global sites. That leaves a second portability problem at the enterprise layer: how the validated decision method, model applicability, SOP authority and approval boundaries travel with the line. Domain Twin™ is designed to make that operating context portable without detaching it from governance.

Domain Twin™ is Profet AI’s implementation of that manufacturer-specific layer. At the point where horizontal industrial AI enters live operations, this layer stops being an implementation detail: it is what keeps context, authority and model applicability consistent as more models, agents and physical systems participate in the same workflow. Domain Twin™ carries those operating semantics, evidence, decision rights and governance boundaries across the industrial AI stack.

In the reference architecture described here, Domain Twin™ serves as the manufacturing domain software layer. It is designed to connect NVIDIA-enabled physical intelligence with the manufacturer’s own knowledge, models, permissions and workflows and preserve that operating context as governed, auditable and reusable AI assets. At scale, what should move from one proof of concept to another line or plant is not an agent transcript. It is a validated decision method: the relevant knowledge, model evidence, operating rules, workflow and governance boundary. That is what turns a horizontal technology foundation into repeatable manufacturing capability without forcing every site to rebuild the same operating knowledge.

From higher-fidelity simulation to repeatable industrial operations

Industrial digital twins will continue to gain physical fidelity, simulation speed and operational reach. Factories also run on accumulated human experience, process knowledge, business rules, security policy and organizational responsibility. If industrial AI is expected to operate consistently beyond a single use case, those elements need a machine-usable and governable representation of their own.

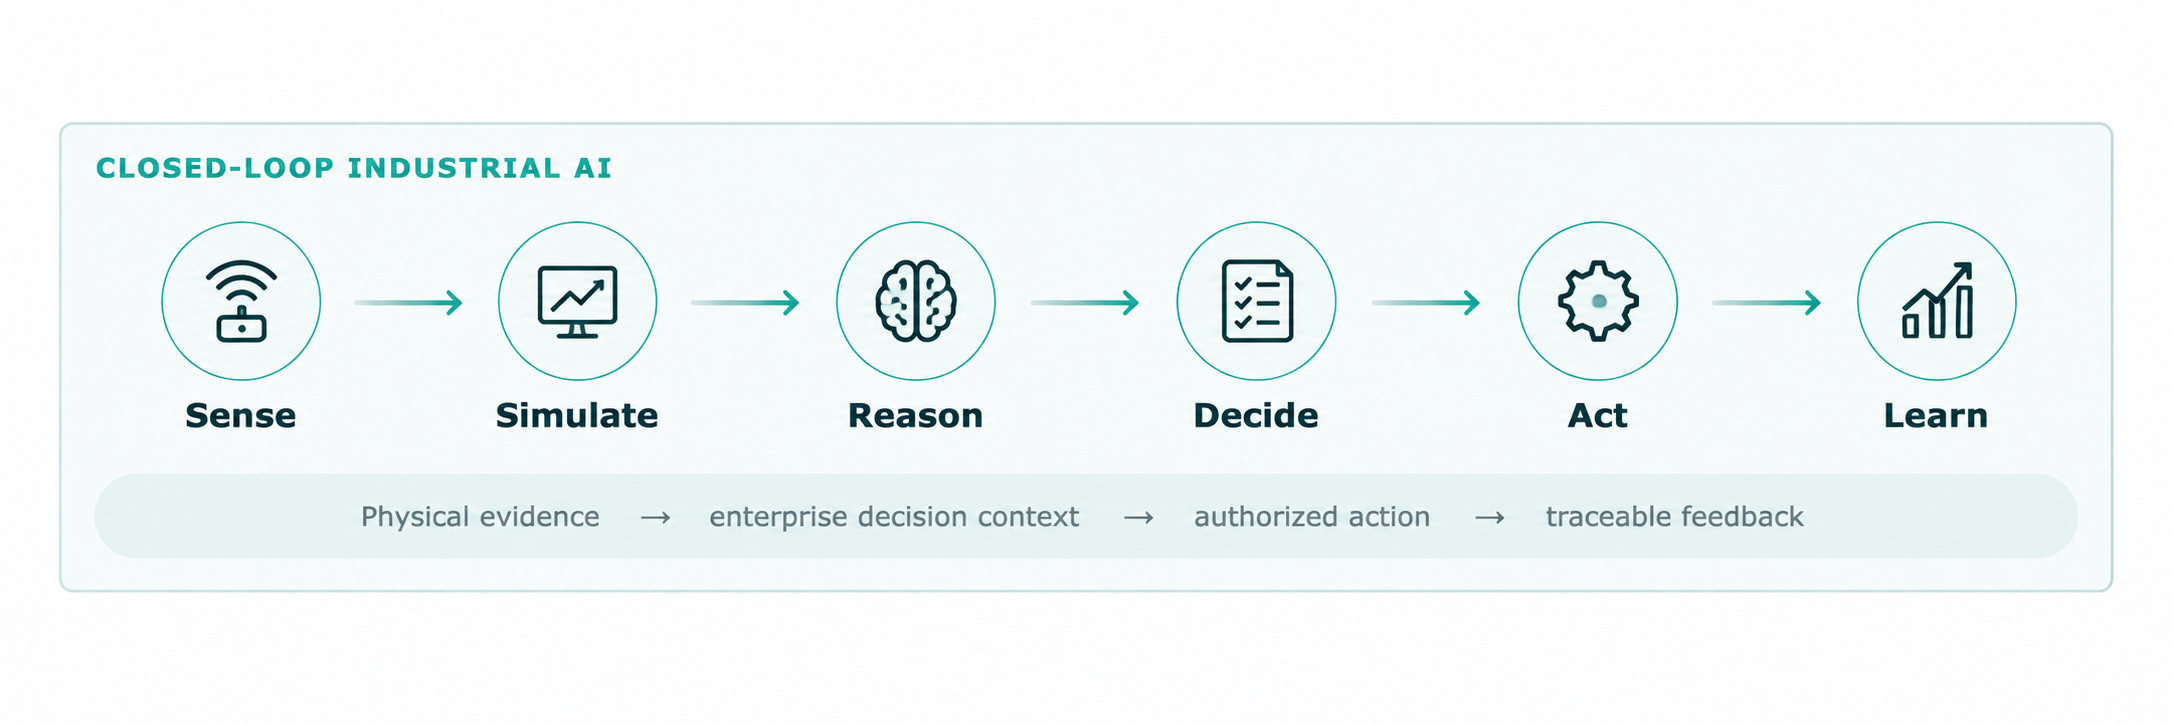
Connecting the twin of the physical world with the twin of enterprise expertise creates a more complete industrial AI loop: sense what is happening, simulate what may happen, reason with enterprise context, decide within policy, act through an authorized path and retain the outcome for the next cycle.

Closed-loop industrial AI: sense, simulate, reason, decide, act and learn, with authorized action and traceable feedback.

Digital twins give Physical AI a world it can observe, simulate and optimize. Domain Twin™ gives industrial AI a durable representation of enterprise expertise, model evidence, permissions and decision logic, with Machine Learning and Agentic AI capabilities operating inside the same governed context. Connected through a closed operating loop, the two create a path from physical intelligence to accountable action and from a successful use case to repeatable deployment across lines and plants. Manufacturing know-how becomes a reusable enterprise asset without losing the evidence, authority and controls that make it trustworthy.

Frequently asked questions

Does Domain Twin replace an industrial digital twin?

No. In this architecture, the industrial digital twin supplies physical state, simulation results and constraints. Domain Twin adds manufacturer-specific knowledge, model evidence, permissions and workflows for governed decisions and actions.

Can an AI agent change equipment settings without approval?

Only actions within the explicitly authorized scope should execute. Process limits, access controls, required human approvals and audit records define the boundary between a recommendation and an equipment or enterprise-system action.

Explore Domain Twin™ for your manufacturing workflow

Explore Domain Twin™, AutoML and AI Studio to map the knowledge, model evidence, system connections and approval points needed for your use case.

From Digital Twin to Domain Twin™: Closing the Industrial AI Loop Read More »

From Semiconductor Know-How to AI ROI: How Manufacturing AI Is Moving into Operations in Penang

From Semiconductor Know-How to AI ROI: How Manufacturing AI Is Moving into Operations in Penang

As Malaysia’s semiconductor industry continues to move up the value chain, manufacturers need AI to move beyond isolated experiments and become part of governed, repeatable workflows.

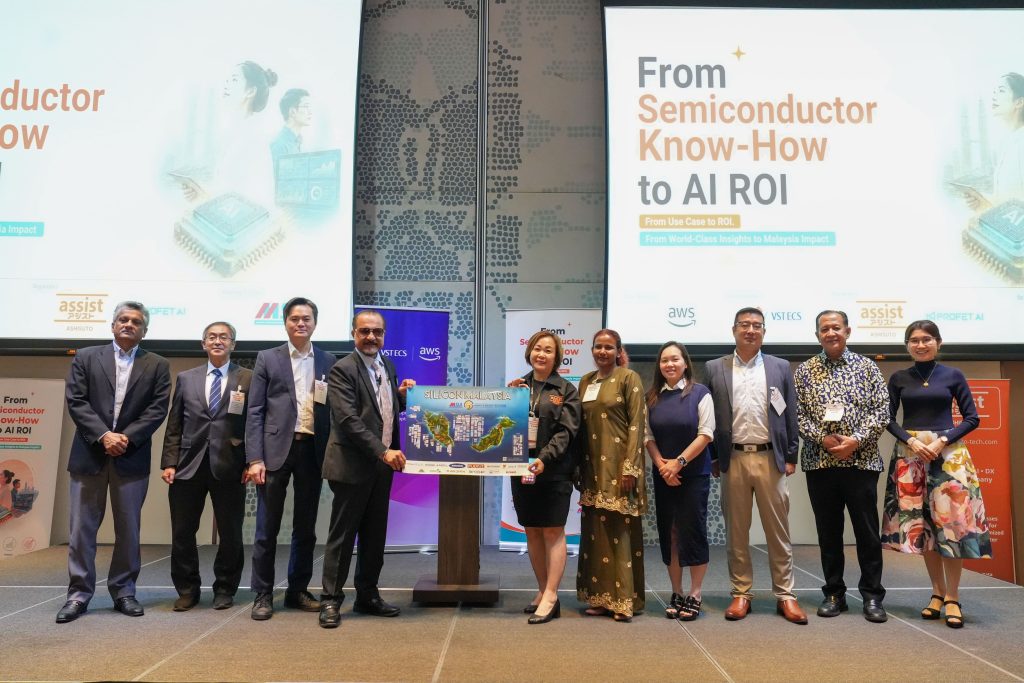
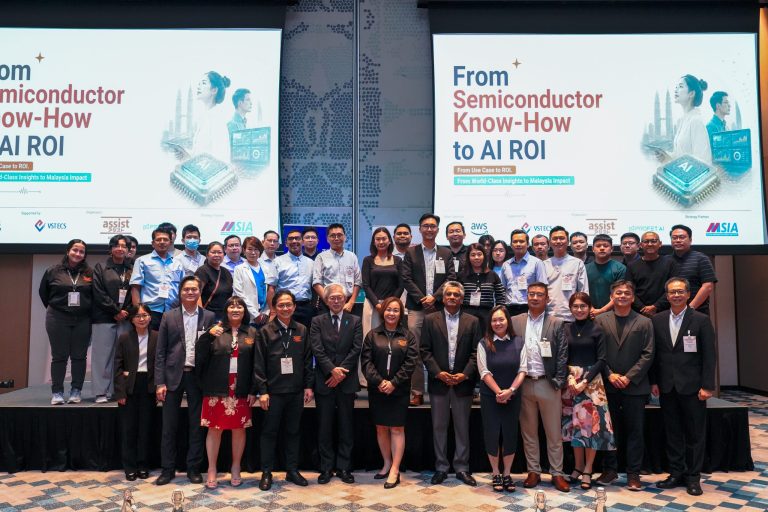
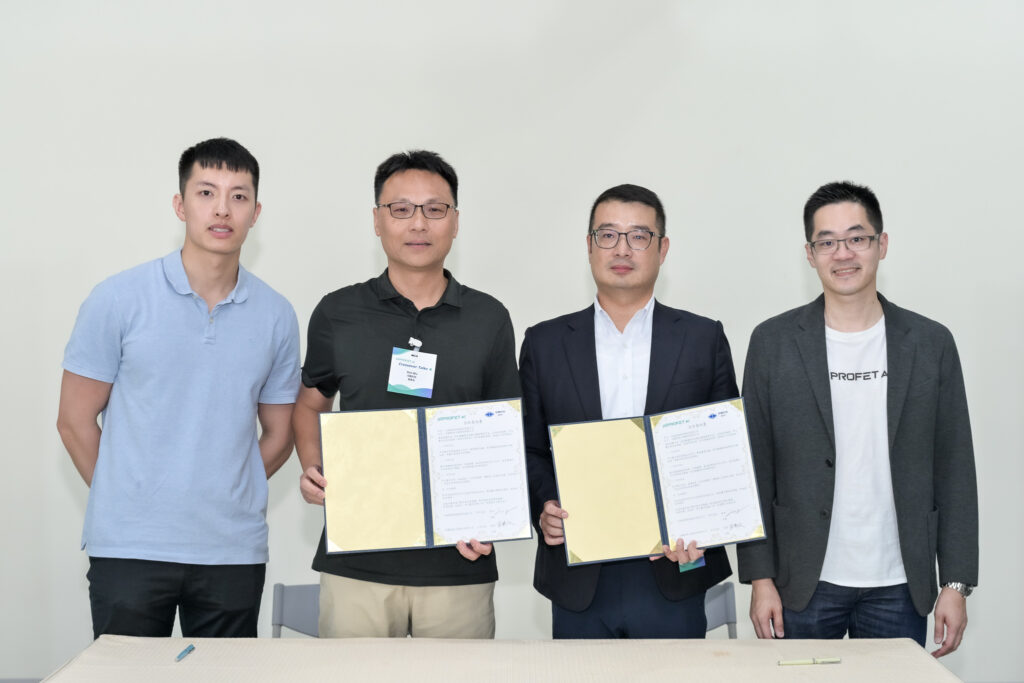
Profet AI and its Malaysian partner, Ashisuto Global Technologies, co-hosted the “From Semiconductor Know-How to AI ROI” forum in Penang, bringing together industry perspectives from Taiwan and Malaysia. The discussion explored how manufacturers can turn frontline expertise into governable, reusable AI assets and move AI from individual use cases toward measurable operational outcomes.

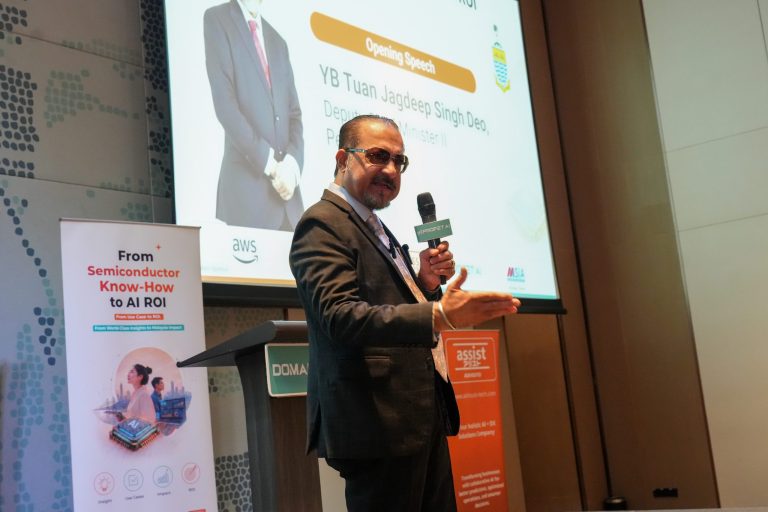
YB Tuan Jagdeep Singh Deo, Deputy Chief Minister II of Penang

The event opened with remarks from YB Tuan Jagdeep Singh Deo, Deputy Chief Minister II of Penang. In his address, he expressed his hope that more Taiwanese companies would continue to establish and deepen their presence in Penang, further expanding cooperation in manufacturing, technology, and talent development.

Penang has become a key hub for Malaysia’s semiconductor and electronics manufacturing industries and is continuing to move into higher-value areas such as IC design, advanced packaging, and advanced manufacturing. For Taiwanese companies expanding into Southeast Asia, the challenge is not only to transfer equipment and production capacity, but also to bring years of accumulated process expertise, quality know-how, and management practices into new manufacturing sites.

What Holds AI Back Is Often Not the Model, but the Gap Between Knowledge and Workflows

Drawing on practical experience from Taiwan’s semiconductor industry, Profet AI Special Assistant to the CEO James Yang noted that despite differences in company size, manufacturing processes, and IT architecture, manufacturers often face similar challenges when scaling AI. These include fragmented data, knowledge scattered across people and systems, difficulty scaling AI projects, and models that remain disconnected from day-to-day workflows.

Profet AI Specials Assistant to CEO, James Yang

“The question is not how many employees are using AI, but whether AI can shorten response time for a specific issue, improve first-pass yield, or help newer engineers make decisions closer to those of experienced engineers,” said Yang. “AI use cases need to start with the problems factories are already measuring. That is how AI connects to real operational value.”

Semiconductor manufacturing is shaped by batch conditions, product specifications, process recipes, equipment status, test programs, and environmental variables. The same sensor reading or inspection result can mean very different things depending on the product, tool, or stage of production. As a result, AI cannot rely on isolated data points alone. It needs to reconstruct the full manufacturing context behind each issue.

Data alone is also not enough. Companies need engineers to keep teaching AI what sound engineering judgment looks like. Models can identify patterns and possible causes, but frontline teams are still the ones who determine whether the evidence is sufficient, which constraints matter, and what action fits the production situation at hand. With each human review and feedback loop, individual experience can gradually be turned into lasting organizational capability.

“Our goal is not to replace people, but to extend what they can do,” Yang added. “When engineering knowledge, decision logic, and workflows are turned into governable, reusable AI assets, critical know-how is no longer confined to a single engineer or a single plant. It can be applied safely across teams and sites under the right governance.”

That thinking sits at the core of Profet AI’s Domain Twin™. Positioned as the enterprise AI brain, Domain Twin™ brings together predictive models, domain knowledge, workflows, and governance into a unified operating layer. AutoML enables engineers to build predictive models from structured manufacturing data through a no-code approach, while AI Studio provides an agentic AI collaboration environment for developing AI assistants, digital employees, and workflow-connected AI applications.

As AI becomes part of day-to-day workflows, governance cannot be treated as an afterthought. Companies need to know who initiated a task, which data, tools, and models the AI used, what actions it took, and what outcomes it produced. Only with a complete record, from identity and access to execution results, can AI scale from a single production line to multi-site and cross-border operations within a controlled, manageable, and auditable framework.

The Next Stage for OSAT Is About More Than Higher Levels of Automation

Taiwan Artificial Intelligence Association advisor Howard Hsieh approached the discussion from the perspective of the OSAT industry, extending it to how companies operate and make decisions. OSAT providers are simultaneously facing advances in packaging technologies, rising product and process complexity, cost and delivery pressures, talent shortages, and supply chain uncertainty. Traditional automation is effective at executing predefined rules, but when production conditions change rapidly and the causes of abnormalities interact with one another, companies need more than faster execution. They need to understand situations and make decisions faster.

AI is therefore beginning to enter a broader range of operational areas, including R&D and process innovation, production and equipment management, quality, supply chain, and energy management. It can help engineering teams narrow the search space for process parameters, identify equipment and quality risks earlier, and provide more timely decision support across orders, capacity, inventory, and energy use.

However, a growing number of AI use cases does not mean an enterprise has completed its AI transformation. If each department builds its own models, data environments, and operating processes, AI can create a new generation of information silos. To scale adoption sustainably, companies need shared AI and data platforms, clear governance and cybersecurity mechanisms, and an operating model that enables engineering, IT, data teams, and management to work together.

Taiwan Artificial Intelligence Association advisor Howard Hsieh

“As AI moves from copilots to coworkers, it becomes part of everyday work and decision-making, while continuing to learn from each round of feedback,” said Hsieh. “What needs to change is not only the system itself, but how companies design workflows, develop talent, and redefine the division of labor between people and AI.”

When equipment shows signs of abnormal risk, AI should do more than generate a prediction. It should be able to pull together relevant process records, compare past cases, recommend an inspection sequence, notify the responsible personnel, and track what happens next. In that sense, the value of AI shifts from simply providing answers to helping work get done.

That does not mean handing every decision over to AI. It means redesigning how people and AI work together. Companies need to clearly define which tasks can be automated, which actions require human confirmation, and which decisions must remain subject to expert review.

For that reason, AI transformation cannot be treated as an IT project alone. It also involves workflow design, decision rights, talent development, and management systems. Once AI becomes part of day-to-day operations, what changes is not just a technology stack, but how the organization understands problems and takes action.

From Industry Adoption to Measurable Operational Outcomes

Duncan Lee, Technical Director of the Malaysia Semiconductor Industry Association (MSIA), shared observations from the local industry, noting that AI adoption among Malaysian companies is increasing. The next stage, however, is to move beyond general-purpose AI tools toward deeper enterprise applications. In semiconductor manufacturing, AI needs to be built on a strong foundation of automation, data, and cross-functional collaboration so that it can support broader manufacturing decisions rather than solve isolated problems.

Tham Kok Tong, COO of Ashisuto Global Technologies, shared examples from Malaysian manufacturers to illustrate the AI adoption journey, from identifying business needs and preparing data to validating applications on the production floor. Whether predicting product defects using process and quality data or assessing equipment conditions through sensor and machine data, these cases shared a common starting point: a clearly defined operational problem tied to measurable indicators.

Companies need to determine whether the problem is linked to actual production or quality metrics, whether sufficient and usable data is available, whether model outputs can be translated into concrete actions, and whether improvements can be continuously measured after deployment. When problems, data, and actions are not connected, even a highly capable model is unlikely to deliver meaningful operational value.

Tham Kok Tong, Ashisuto Global Technologies

The Real Challenge Is Bringing AI Into Everyday Decision-Making

The event concluded with remarks from Shinya Machida, Consul-General of Japan in Penang, bringing to a close an exchange that connected industry perspectives from Taiwan, Malaysia, and Japan.

Across technology, talent, and operational processes, the real challenge for manufacturers is not to launch another PoC, but to bring AI into everyday decision-making and continuously deliver measurable operational outcomes.

Profet AI will continue to bring Taiwan’s manufacturing AI experience to more markets, working with local partners and manufacturers to turn frontline know-how into governable, reusable AI assets and move AI from individual use cases to ROI.

From Semiconductor Know-How to AI ROI: How Manufacturing AI Is Moving into Operations in Penang Read More »

Profet AI Drives Significant Efficiency in R&D for Chyi Ding, Accelerating Differentiation and Competitive Edge

Nicholas Su, Special Assistant to the Chairman and Acting Spokesperson of Chyi Ding Technology, explaining the necessity of integrating AI into the company’s future development.

Founded in 2003, Chyi Ding Technology specializes in advanced temperature control and AMC (Airborne Molecular Contaminants) removal technologies, serving semiconductor precision environment control and energy-saving engineering sectors. With a robust R&D team, Chyi Ding has garnered numerous accolades, including the Taiwan Excellence Award and MOEA’s SME Innovation Research Award, totaling 33 awards. Its clientele includes the world’s top semiconductor manufacturers and packaging and testing facilities, with customers spread across Taiwan, the US, Germany, Switzerland, Japan, Korea, and Singapore.

“We’ve always been at the forefront of precision temperature control, and in many areas, we’re even regarded as world leaders. However, to push our technology even further, external support is essential,” explains Nicholas Su, Special Assistant to the Chairman and Acting Spokesperson of Chyi Ding Technology. Currently, Chyi Ding is primarily focused on precision temperature control for semiconductor manufacturers and packaging and testing facilities, particularly for exposure and coating machines. As semiconductor manufacturers produce ever-smaller chips, demand for high-precision temperature control equipment from these companies will continue to grow.

Pursuing Advanced R&D: Deciding to Implement AI

“The more precise the manufacturing process, the more critical temperature control becomes,” explains Su. He offers a simple comparison: a strand of hair is about 50,000 nanometers in diameter, whereas TSMC’s current chips are manufactured at just three nanometers. In such an environment, even the slightest change in temperature or humidity can cause thermal expansion or contraction, compromising the wafer yield.

Given that Chyi Ding’s clients are globally recognized semiconductor and packaging/testing giants with stringent requirements, the company continuously seeks breakthroughs and innovations in R&D. “Our competitors are all foreign companies, primarily from Japan,” Su says. As the first and only company in Taiwan to domestically manufacture precision temperature control equipment, Chyi Ding began exploring the potential of AI three years ago as a way to refine their technology and meet the high standards expected by clients.

Su recalls venturing into an entirely new field: “At that time, no one in the company had any experience with AI!” To familiarize himself, Su began experimenting with ChatGPT, initially using it to resolve some legal queries. Eventually, he encouraged colleagues to use ChatGPT to tackle work-related challenges, noticing a significant boost in their productivity. This discovery led him to seriously consider the potential of AI to enhance R&D capabilities at Chyi Ding.

7 Days to Solve a Year-long Roadblock: Profet AI AutoML Significantly Boosts R&D Efficiency

In early October 2023, after evaluating several AI platforms, Chyi Ding decided to implement Profet AI’s AutoML platform. For them, the main goal was to shorten the timeline for R&D advancements and identify overlooked aspects of their research—a task Profet AI’s AutoML platform was well-suited to address.

Nicholas Su explains with an example from their precision temperature control project. They had been working on a research initiative for two years to improve their equipment’s temperature control from ±0.01°C to ±0.001°C. While this adjustment might seem minor, adding an extra decimal point required a whole new level of precision, which had stalled the team for over a year.

He elaborates that precision temperature control is a highly challenging field. Any minor change in airflow or refrigerant flow causes fluctuations in the system’s parameters. “Our team kept hitting a ‘wall,’” Su recalls. “Every time we adjusted one parameter, another would shift, making it impossible to reach the target value.”

The turning point came when the R&D team input all parameters into Profet AI’s platform for analysis. They discovered that some parameters, previously thought to be crucial, were actually insignificant. By identifying key factors and simulating an AI model, the team achieved the ±0.001°C precision within a week. Profet AI’s platform dramatically boosted the R&D team’s efficiency, helping them overcome a year-long hurdle in just seven days.

Profet AI Workshops Facilitate AI Implementation and Streamline Training

Profet AI’s platform was selected primarily due to its user-friendly design and extensive track record. Nicholas Su noted that many of Profet AI’s existing clients overlap with Chyi Ding’s, indicating that Profet AI not only possesses deep industry knowledge but also understands the unique pain points and challenges of semiconductor companies.

In the initial phase of implementing Profet AI, a series of AI workshops were conducted, where professional consultants guided Chyi Ding’s employees in data organization, data application on the AI platform, and selecting suitable models to deploy AI projects across various departments. Su highlighted that many participants in this first round of workshops were not engineers but came mainly from business backgrounds, such as HR and marketing. Yet, by the end of the sessions, these employees had become proficient in using Profet AI’s platform—a remarkable transformation.

Looking ahead, Chyi Ding aims to leverage Profet AI’s tools and methodologies to digitize the expertise of senior employees across departments. By doing so, they hope to significantly reduce the training time for new hires. Instead of learning every step from scratch, new employees can start from an advanced point, allowing them to build on existing, systematized knowledge from the get-go.

Secure Implementation of Profet AI with No Data Leakage  

With multiple research and development patents, Chyi Ding initially had concerns about potential data leakage of its proprietary technology when adopting AI. Nicholas Su explained that Chyi Ding, as an R&D-focused company, has around 60 design and research personnel, representing a quarter of its workforce. Given that many of the company’s technologies are self-developed, Chyi Ding places great importance on the management of patents and trade secrets, recently achieving Taiwan’s TIPS A-level certification for intellectual property management. 

However, Su noted that not all technologies or know-how are suitable for patent applications, which heightened concerns about data security when integrating AI. To address these concerns, Profet AI tailored its implementation plan to host servers within Chyi Ding’s premises, ensuring data remains in-house. This setup allows Chyi Ding to confidently leverage the Profet AI platform, significantly enhancing R&D efficiency and empowering the company to establish a strong competitive edge globally.

Profet AI Drives Significant Efficiency in R&D for Chyi Ding, Accelerating Differentiation and Competitive Edge Read More »

,
Dr. Bey Yu from Wiwynn

Wiwynn Drives a Bottom-Up AI Culture with Profet AI, Rapidly Cultivating AI Talent

Wiwynn Drives a Bottom-Up AI Culture with Profet AI, Rapidly Cultivating AI Talent

Dr. Bey Yu from Wiwynn

Wiwynn, specializing in solutions for hyperscale data centers and cloud IT infrastructure, counts Meta, Microsoft, and other major U.S. cloud service providers (CSPs) among its primary customers. Benefiting from the widespread adoption of cloud applications, Wiwynn has experienced rapid revenue growth in recent years.

To provide these customers with highly efficient, low-energy consumption solutions for large-scale computing and storage, fast data transmission, and hardware-software integration, Wiwynn adopts an Original Design Manufacturer (ODM direct) model. This approach delivers customized server motherboard designs, production, and assembly services tailored to customer workloads.

“Improving efficiency and agility is very important to us,” emphasized Dr. Bey Yu, Director of Information and Digital Technology at Wiwynn. Following the company chairman’s directive from five years ago, Wiwynn has pursued a “top-down strategy and bottom-up execution” to drive digital transformation. This includes fostering an “AI-for-All” approach, encouraging employees to embrace digital tools, and establishing an End User Computing culture.

Complex Product Engineering and Resource-Intensive Quotation Process Streamlined by AI

As an ODM direct business, Wiwynn often faces labor-intensive and complex quotation processes whenever customers request quotes.

Yu explained that customer inquiries usually involve new product developments, specifying configurations and expectations while requesting quotes from Wiwynn. Upon receiving such requests, the company needs to send the specifications to all relevant units, asking them to identify and quote components meeting customer requirements. These components range from large items like product casings, metal and plastic parts, to smaller ones like cables and connectors on motherboards. The accumulated costs of these components significantly influence the final quotation. A well-done quotation results in profits; conversely, overly high quotations scare customers away, while low quotations lead to losses.

“Quotation often consumes a lot of our manpower,” Yu said. A single product quotation typically requires weeks of information gathering from multiple layers, followed by senior sales staff estimating reasonable quotes. This process is far from agile.

Thus, when Wiwynn decided to implement AI in early 2024, improving the quotation process became a key initiative. With the assistance of AI models, the relevant departments could more efficiently estimate optimal components and prices, reducing the quotation process time by 30%. Moreover, Wiwynn aims to digitize domain knowledge—previously reliant on a few senior employees—using the AI platform to accelerate talent development across departments.

Yu cited an example involving the quotation of product structural parts. One major expense in structural parts is molds, which require experienced engineers to evaluate the raw materials and processes needed to meet customer requirements. Such expertise is difficult to cultivate, with only a few “key players” in the company. Losing them could lead to significant setbacks.

Profet AI AutoML’s Ease of Use and Expert Advisory Enhance AI Analytical Skills

To significantly enhance efficiency and agility, Wiwynn introduced Profet AI’s AutoML Data Scientist Platform in early 2024. Part of the NVIDIA ecosystem, Profet AI’s platform was selected for its high usability—it requires minimal IT expertise to get started. Another reason was Profet AI’s team of consultants with extensive industry knowledge. Collaborating through AI-ML Thinking workshops with Profet AI consultants, nearly 100 domain experts at Wiwynn produced about 30 AI topics.

Although Wiwynn has trained some AI specialists, Yu admitted that these resources are insufficient to meet the demands of numerous AI projects. Furthermore, these specialists lack insight into the operations and challenges of various departments, such as manufacturing, sales, and finance. Profet AI’s consultants, with their deep industry knowledge and AI implementation experience, enable domain experts in different departments to quickly adopt AI.

“The value of consultants is in guiding teams to think,” Yu said. Profet AI’s consultants assist users in identifying areas where AI can be applied, clarifying key factors influencing AI, and pinpointing highly relevant data. Developing these analytical skills is something Wiwynn’s in-house AI talent could not achieve alone.

AI Workshops Attract Over 100 Participants, Boosting R&D Efficiency and Realizing AI-for-All Goals

Earlier this year, with Profet AI’s support, Wiwynn organized a series of AI workshops. Initially, 7–8 teams were expected to participate. However, within a month, over 20 teams and about 100 people signed up to explore AI topics for their respective departments. After months of validation, around 10 AI projects are expected to materialize.

In addition to AI applications in quotations, AI projects in engineering R&D and factories have also matured. During the workshop competition, one R&D team applied AI to thermal management. They’ve drastically reduced the time required to determine optimal parameters by half with the help of Profet AI’s platform. Another team proposed factory production line optimization, using the Profet AI platform to swiftly adjust line configurations, such as workstation layouts and machine allocations, achieving operational excellence.

Yu noted that months of AI workshops have led to increasing departmental engagement in AI initiatives. Moving forward, Wiwynn plans to recruit a second batch of AI seed talents and invest more in AI talent development. Currently, Wiwynn is collaborating with Profet AI consultants to establish a cross-departmental virtual organization called the “Center of Excellence (CoE).” This organization will facilitate knowledge sharing and experience exchange among employees involved in AI projects, supported by professional consultants to resolve challenges and accelerate AI implementation across departments.

After establishing a robust AI adoption mechanism in Taiwan, Wiwynn aims to extend this model to its global operations, fully realizing the chairman’s vision of “AI-for-All.”

Wiwynn Drives a Bottom-Up AI Culture with Profet AI, Rapidly Cultivating AI Talent Read More »

Steven Yan, BenQ, at Crossover Talks Taoyuan

BenQ Enhances Inventory Forecasting Accuracy Over 80% with Profet AI Platform

BenQ Enhances Inventory Forecasting Accuracy Over 80% with Profet AI Platform

Steven Yan, Sr. Manager of Information Technology Service Center at BenQ’s Enterprise Services Department

As AI technology advances, its applications are transforming diverse industries. In 2024, BenQ, a subsidiary brand of Qisda Corporation, embarked on integrating AI capabilities. Recognizing the critical role of product maintenance in brand loyalty, BenQ implemented an AI strategy two years ago to optimize supply chain management. Leveraging AI to forecast future maintenance part demands enables BenQ to make accurate predictions based on historical data and market trends while dynamically adjusting models to address sudden demand changes.

“Managing repair part inventory without precise control creates significant cost pressures,” said Steven Yan, Sr. Manager of Information Technology Service Center at BenQ’s Enterprise Services Department. BenQ’s products have warranty periods ranging from two to five years, extending up to seven years for B2B clients. In the past, experienced technicians forecasted three-year repair part stock requirements based on product sales and repair data, aiming to minimize dead stock costs and prevent shortages that could increase repair costs and impact customer loyalty.

Creating a “Digital Master” for Supply Chain Management to Significantly Reduce Excess Inventory Costs

To improve inventory forecasting accuracy and ensure data-driven decision-making, BenQ opted for an AI-driven approach to supply chain management. Initially, other AI platforms were tested, but due to usability challenges and the need for extensive IT involvement, the results fell short of expectations. After exploring Profet AI’s AutoML platform, BenQ was impressed with its user-friendly interface, high model performance, and the dedicated support from Profet AI’s manufacturing-experienced consulting team, leading to a quick decision to adopt the platform.

“Profet AI’s software significantly reduces our dependence on IT staff and data scientists,” noted Yan, “empowering the supply chain department to effectively forecast future maintenance part inventory needs, achieving a forecast accuracy exceeding 80% and saving substantial inventory costs annually.”

AI Workshop Speeds Internal Talent Development

BenQ’s successful and seamless AI adoption was bolstered by Profet AI’s team-led AI-ML workshops. “Consultant support was crucial,” Yan remarked, adding that initially, employees feared AI’s learning curve would be steep. However, Profet AI’s team guided participants through practical methodology over three months, allowing employees without IT backgrounds to ideate on real business scenarios, identify key parameters for modeling, and optimize workflows. The workshops fostered a cohort of ‘citizen data scientists,’ ensuring successful AI integration within the company.

AutoML Helps Optimize Customer Profiles for More Precise Digital Marketing

After successfully resolving supply chain challenges, BenQ applied Profet AI’s advanced algorithms to its digital marketing strategy six months ago, further transforming its business.

Yan explains that BenQ previously utilized various tools to collect and analyze consumer data. These included RFM modeling to segment customers by recency, frequency, and monetary spend, Google Analytics (GA4) for tracking website engagement and conversion flows, and a Customer Data Platform (CDP) for consolidating first-party data. This data spanned customer activity across BenQ’s official website, e-commerce, customer service, and event systems, creating detailed customer profiles.

With these customer profiles now quantified into actionable insights, BenQ leverages Profet AI’s algorithms to predict product purchase probabilities. This approach enables BenQ to identify customer behavior patterns, such as paths taken by converted and unconverted customers. Once customers engage with any touchpoint on the sales platform, BenQ can anticipate purchase likelihood within specific timeframes and strategically present incentives to encourage conversion.

Following the success of AI-enabled digital marketing, Yan notes that BenQ has been expanding Profet AI’s platform to address predictive tasks in other departments. For example, Profet AI’s algorithms have streamlined product parameter adjustments in R&D, significantly reducing development time.

Looking ahead, BenQ envisions creating “digital experts” across all divisions with Profet AI’s AutoML platform, empowering each team to independently initiate AI-based modeling and testing for critical challenges. This vision aims to foster agility, drive efficiency, and support sustained operational growth.

BenQ Enhances Inventory Forecasting Accuracy Over 80% with Profet AI Platform Read More »

8 Ways that Taiwan Manufacturers are Using AI to Navigate Economic and Geopolitical Uncertainty

Geopolitical chaos and a looming economic downturn are a growing concerns for manufacturers, given their complex and global operations. Recent threats faced to supply chains, include inflation, trade disputes, war, pandemics, and energy access. A push for rapid decoupling also creates serious headaches for decision-makers.

Taiwan: The Epicenter of Both Geopolitical Uncertainty and AI Technology 

In the face of these challenges, manufacturers in Taiwan are turning to AI to navigate this increasingly complex global economic landscape. Recently, a four-part summit titled Crossover Talks, organized by manufacturing AI solution provider, Profet AI, brought together industry, academia, and technology experts to discuss the opportunities, challenges, and best practices for manufacturers to implement AI and digital transformation in a challenging economic climate.

Taiwan has some of the most advanced manufacturers in the world and is obviously at the forefront of some of the most worrying geopolitical tensions. It is also at the cutting edge of the technologies that will power the AI revolution, such as semiconductors, which makes it the ideal location for this discussion.

Keynote speakers included experts from AUO, Innolux,Gogoro, Cheng Shin Rubber, Kuan Yuan Paper, Asia Giant Engineering, De Licacy Industrial, Taiwan AI Academy, National Cheng Kung University, National Taiwan University, and Feng Chia University.

8 Takeaways

Profet AI has diluted the four events and hours of discussion into eight key takeaways:

  1. Successful Digital Transformation Requires the Marriage of Data Science and Domain Knowledge

Data science teams in enterprises need to work in conjunction with departments and colleagues with vertical domain knowledge. Profet AI preaches that successful digital transformation relies on the use of the correct data combined with domain knowledge in order to generate the actionable intelligence that can drive decisions.

  1. Prioritize Cross-Department Conversation

For an enterprise to successfully carry out digital transformation, it needs the support of management and effective dialogue and cooperation between departments.

  1. Foster a Habit of Data Collection

For traditional companies to become more data-driven, they need to first start analyzing their existing data and also foster a culture of data collection. Stakeholders need to believe in the power of data to engender change, and there also needs to be an investment in the correct AI tools.

  1. Focus on First Using AI to Solve Key Problems, Not Changing the Whole Company

Companies should avoid seeing AI as a panacea to turn the company around. Instead, they should prioritize specific processes that need to be optimized.

  1. Use AI to Replicate the Knowledge of ‘Old Masters’

Traditional manufacturers often over-rely on the wisdom of senior staff, which makes them vulnerable when processes need to be replicated or there needs to be a handover of know-how if they retire. Data-driven companies can utilize AI to create a framework for both personnel succession and the handover of knowledge.

  1. Let Data Enhance Personnel Management

Participants at the summit complained in recent years, being blighted by worker shortages. Companies can utilize AI to highlight the characteristics of workers that have resigned and which present workers have a high probability of leaving, then reach out to them in advance to see if there is any way to help them.

  1. Manufacturers Need to Recruit and Cultivate AI Talent

For digital transformation to be successful, manufacturers need to change their internal culture and also cultivate their own AI talent. Over the last five years, AUO has trained more than 1,000 AI engineers in a joint initiative with the Taiwan Artificial Intelligence Association (AIA).

  1. Everything Begins with Company-Wide Mindset Change

Director of AIA, Benjamin Kuo, believes that as well as fostering AI talent, there needs to be a mindset change in top management so that the company will become a data-driven organization. Only once the company has both the AI mindset and talent can they really lay the blueprint for digital transformation. Leaders need to ensure that AI is embedded into the DNA of their organizations.

8 Ways that Taiwan Manufacturers are Using AI to Navigate Economic and Geopolitical Uncertainty Read More »

Guests at Profet AI Crossover Talks

Wiwynn Reduces Labor Costs in Component Pricing with AI; Mighty Electronics Achieves New Production Efficiency Using AutoML Platform

Global Server Leader Fosters an “All-in AI Culture” through AI-ML Thinking Workshops; User-Friendly AI Empowers a 30-Year SMT Veteran to Successfully Transform into a Hardware Innovation Hub

Guests of Crossover Talks EMS

The adoption of AI applications in enterprises is already underway in Taiwan. The most pressing issue is how to leverage various resources to empower employees quickly and establish an internal AI culture.

Profet AI, recognized as one of the Top 100 Startups of 2024 and deeply rooted in the AI software market for manufacturing, recently hosted a dedicated Crossover Talks EMS event titled “Straight Talk! Ask Us Anything About Real-World AI Implementation Experiences!” The event featured experts from industries such as Wiwynn, a global leader in cloud servers; Mighty Electronics, a renowned EMS brand with 30 years of experience; and Super Dragon, Taiwan’s first publicly listed environmental technology company.

These industry leaders shared their comprehensive journeys from initial AI adoption to subsequent promotion, offering authentic insights to the audience. Through practical case studies and a live Q&A session, attendees gained a deeper understanding of the challenges in promoting AI within the industry and sparked ideas for further innovative AI applications.

Comprehensive Team Engagement: Wiwynn Boosts Talent Quality through AI Machine Learning Workshops
Dr. Bey Yu, Director of Information and Digital Technology at Wiwynn, Shares Insights on AI Adoption

Dr. Bey Yu, Director of Information and Digital Technology at Wiwynn, shared the company’s motivations and strategies for AI adoption. He emphasized that Wiwynn’s core principle is “strategy from the top down, execution from the bottom up.” He highlighted that promoting AI should start small and gradually expand across the organization by connecting AI teams horizontally, ultimately integrating it into the company culture.

Dr. Yu mentioned that the rise of generative AI in 2022 spurred Wiwynn to actively pursue a company-wide AI initiative. To achieve this goal swiftly, the company chairman personally oversaw the effort, mobilizing all departments and establishing a Center of Excellence (CoE) as a dedicated team for AI promotion while seeking external collaborations.

Being a key player in NVIDIA’s supply chain, Wiwynn collaborated closely with Profet AI to accelerate AI technology adoption. Wiwynn valued Profet AI’s extensive expertise in the manufacturing industry and decided to partner with them. Profet AI’s experienced consulting team and industry-specific AI implementation methodologies guided Wiwynn’s team in brainstorming actionable AI topics. Over a four-month AI workshop, nearly 100 domain experts across different teams built close to 800 predictive models and successfully generated nearly 30 AI topics.

While simultaneously validating the feasibility of these AI topics, Wiwynn successfully established a culture of AI engagement, enabling non-IT employees to use data-driven thinking to improve their current work processes. Dr. Yu shared that many successful topics were related to cost estimation. Previously, the component pricing process required over 20 personnel; now, with AI effectively leveraging historical data, they can quickly build models and provide quotes on demand, significantly enhancing operational efficiency.

Another beneficial topic was the optimization of experimental parameters in the R&D department. Engineers used to spend an entire day on repetitive tests, but now AI suggests optimal parameters, greatly reducing experimental costs. Dr. Yu emphasized that the key to AI adoption is not just short-term ROI but also improving employee quality, reinforcing the importance of data, and shifting mindsets, thereby forming a culture that serves as the foundational strategy for long-term AI promotion.

A Champion of Hardware Innovation: Mighty Electronics Expands Its AI Culture from Point to Area
Ray Tai, Vice President of Mighty Electronics and CEO of Mighty Innovation, Shares Real-World AI Implementation Experiences

Ray Tai, Vice President of Mighty Electronics and CEO of Mighty Net, shared the company’s real-world experiences with AI adoption. He recalled how, under the guidance of consultants, the company began experimenting with AI in 2019, starting with small-scale applications and gradually expanding to automated deployments, helping employees transform their thinking patterns.

When the pandemic suddenly broke out, significant adjustments to personnel arrangements were necessary, prompting the company to embark on a series of digital transformations. Tai personally led the initial push for digitization, helping employees transition from paper-based operations to automation. He pointed out that the biggest challenge in digital transformation is changing habits, so it’s crucial to lower the barriers to entry.

The simplicity and user-friendliness of Profet AI’s tools have been the primary reason for their ongoing collaboration since 2019. In the initial phase of transformation, Tai aimed to first address supply chain-related pain points, selecting employees with a stronger data mindset as the first batch of seed members, and then gradually expanding AI data thinking to other operational departments.

Tai mentioned that the greatest benefit of AI adoption has been enabling employees to gradually establish a data-driven mindset. He cited an example of transitioning from “manually recording lunch orders” to “scanning QR codes to order meals.” While this shift in daily habits may seem minor, it gradually establishes an internal AI culture, preparing every domain expert for the best transformation and upgrade.

Beyond building a habit of data thinking, AI has also helped the Mitec team uncover new key factors that had previously gone unnoticed. For example, when addressing issues with SPI printers, the lack of effective data initially hindered model performance. However, by involving on-site personnel directly in the AI modeling process, they identified unexpected key factors, effectively improving data collection quality and model performance. These outcomes, from starting at a single point to laying a foundation for expanding to broader applications, reflect the company’s commitment to digital and AI transformation, paving the way for a solid future in comprehensive AI applications.

Strategic Partnership with Super Dragon: Deepening Smart Applications in Renewable Energy and ESG
Profet AI and Super Dragon Formalize Partnership

Profet AI and Super Dragon formalized a partnership at the forum, committing to jointly advancing smart applications in areas ranging from waste management to renewable energy. Super Dragon President Ken Wu also shared how the company integrates storage technologies for renewable energies such as solar and wind, as well as virtual power plants and other smart applications, and plans to incorporate more AI technologies to create a more comprehensive renewable energy service system. President Wu noted that these innovative applications are not only Super Dragon’s proactive exploration in the ESG field but also represent a smarter future development path for the industry.

This Crossover Talks event provided a platform for in-depth exchanges of practical experiences in the EMS industry. Through on-site discussions and field visits, participants gained a more intuitive understanding of AI and ESG initiatives’ specific applications in the industry. Profet AI will continue this series of events, bringing more practical cases and expert insights to the industry, exploring the limitless possibilities that AI brings to industrial upgrading.

Wiwynn Reduces Labor Costs in Component Pricing with AI; Mighty Electronics Achieves New Production Efficiency Using AutoML Platform Read More »

Profet AI Leads the Way: Four Key Strategies for AI Transformation in Businesses Amidst Economic Uncertainty

Amid growing global economic uncertainty, Profet AI Co-founder and CEO Jerry Huang reflected, “Since 2022, we have traveled across Asia and, through exchanges with numerous companies, deeply felt the pressure and challenges they face in talent upgrading and global expansion. These businesses urgently need to understand how AI can help them proactively deploy strategies and make critical decisions. This experience has strengthened my belief that our 2022 Crossover Talks: AI & the Economic Cycle series was crucial in helping companies identify opportunities amid economic cycles.”

Pain Points and Critical Analysis: Hsing-Chien Tuan and Dr. Chia-Yen Lee Discuss Transformation Strategies at Crossover Talks

In Crossover Talks: AI & the Economic Cycle, Hsing-Chien Tuan, Honorary Chairman of Innolux Corporation, highlighted that even in downturns, businesses should focus on automation, IoT, big data, and AI. He stressed, “Identify pain points with precision, articulate them scientifically, and set meaningful indicators.” Dr. Chia-Yen Lee of NTU added that AI must now be integrated beyond manufacturing into R&D, advising businesses to understand core strengths, explore global and cross-industry expansions, and embrace disruptive technologies.

Dr. Chia-Yen Lee, from the Department of Information Management at NTU, offered profound insights from both academic and practical perspectives. He stated, “Recently, while consulting with semiconductor manufacturers, I often mention that we used to only need to modify the manufacturing site, but now we need to involve AI, even in research and development, and the future potential may be even greater.” Dr. Lee proposed four key actions: first, businesses should deeply understand their core competencies and invest in key areas; second, when expanding, consider international layout and cross-industry expansion; third, explore new markets through geographic expansion; and finally, integrate disruptive technologies and establish new businesses or services through mergers and acquisitions, while paying attention to retaining talent and ensuring the long-term value of technology.

Dr. Lee further suggested that businesses should embark on their AI journey from five aspects: accelerating time (building a digital nervous system), increasing efficiency (promoting digital transformation and intelligence), improving quality (building a learning organization and strengthening education and training), increasing revenue (achieving production-sales balance), and reducing costs (reducing variation and risk).

Asia-wide Consensus Spanning Two Years: PacRim Group Shares the Inevitability of AI Transformation from a Thai Perspective

This perspective extends across Asia. At the 2024 AI Leadership Summit in Bangkok, Porntip Iyimapun, CEO of PacRim Group, a pioneer in global leadership development and cultural transformation with nearly 30 years of experience, presented similar views: “Digital transformation, leadership transformation, and corporate culture transformation are all important parts of the same plan. The introduction of AI is inseparable from these transformations. Thai enterprises need to make comprehensive adjustments in these areas to successfully integrate AI into their business strategies. Without adopting AI, enterprises will gradually be eliminated.” It not only reflects PacRim Group’s professional insights in leadership development and cultural transformation but also confirms the core position of AI in modern enterprise transformation.

AI Helps Businesses Address Economic Challenges and Future Growth

In Profet AI Crossover Talks, multiple companies shared successful cases of using AI tools. Brandon Yeh, Vice Chairman of De Licacy, shared how AI can be used to achieve technology transfer and solve talent recruitment difficulties. Richard Hsieh, Associate Manager of Kuan Yuan Paper, introduced an innovative management method combining OKR, zero errors, and AI. Kenny Chiu, Deputy General Manager of Shuttle Service, shared the experience of using AI to predict and reduce employee turnover.

These cases clearly demonstrate the application potential of AI in various industries and fields. From manufacturing process optimization to human resources management, AI is helping businesses address various challenges, improve efficiency, reduce costs, and prepare for future growth.

Profet AI Leads the Way: Four Key Strategies for AI Transformation in Businesses Amidst Economic Uncertainty Read More »

AI Drives Thailand Market Innovation: Taiwanese Expertise Tailors Solutions

Driven by global economic shifts and the digital transformation wave, AI has become a core tool for businesses worldwide to maintain competitiveness. Thailand, with its strategic geographic location and thriving automotive, food manufacturing, and retail industries, presents immense potential and demand. For the first time, Profet AI, in collaboration with HexaTech Solutions and PacRim Group, hosted an AI Leadership Summit in Bangkok, sharing Taiwan’s successful experiences to tailor AI solutions for the Thai market and facilitate talent training and upgrading.

Speakers at the AI Leadership Summit (from left to right: Chalermkit Rochanavibhata, partner at PacRim Group; Dr. Sampan Silapanad, president of the Electronics and Computer Employers Association; Dr. Howard Hsieh, secretary-general of the Taiwan AI Association; Jonathan Yu, global business manager at Profet AI)
Learning from Taiwan’s Success: Three Key Elements of Digital Transformation

Taiwan’s successful digital transformation offers valuable insights. Dr. Howard Hsieh, secretary-general of the Taiwan AI Association, pointed out that AI is not merely an IT project but requires full engagement and talent upgrading. Taking Innolux 4.0’s digital transformation as an example, the integration of technology, methodology, and mindset (organization and people) is crucial. Taiwan’s experience demonstrates that successful digital transformation requires technological advancements, methodological applications, and continuous optimization of organizational culture, enabling the transition from small-scale projects to full-scale implementation and achieving the status of a lighthouse factory.

Thailand’s AI Landscape: Urgent Need for Transformation to Remain Competitive

In Thailand, the urgency of digital transformation has garnered widespread attention. Dr. Sampan, president of the Electronic & Computer Employers’ Association, emphasized that Thai businesses risk being eliminated from the market if they fail to adopt AI swiftly. He stated, “I envision that within the next five years, over 50% of Thai companies will be AI-oriented; otherwise, Thailand will disappear from the map. This will be the key to entering a highly competitive world.” This perspective underscores the decisive impact of AI on the competitiveness of Thai businesses.

Tailored AI Solutions: Creating Custom Solutions for the Thai Market 

To address the specific needs of the Thai market, Profet AI, HexaTech Solutions and PacRim Group have provided tailored AI solutions that not only meet the market’s practical demands but also encompass applications from business innovation to R&D, helping Thai businesses navigate future challenges. Additionally, Porntip Iyimapun, CEO of PacRim Group, added that digital transformation, leadership transformation, and corporate culture transformation are integral parts of the same plan. She emphasized that AI implementation is intertwined with these transformations, and Thai businesses need to make comprehensive adjustments in these areas to successfully integrate AI into their business strategies.

Facilitating Talent Training and Upgrading: Laying the Foundation for Digital Transformation

The success of digital transformation hinges on the skill enhancement of the workforce. PacRim Group, with 30 years of experience, will focus on providing professional training to equip Thai employees with AI skills and foster an AI-ready culture. This will lay a solid foundation for the long-term development of Thai businesses, ensuring that the entire workforce possesses the capabilities required for the AI era. The digital transformation and AI applications of local businesses will set new benchmarks.

AI Drives Thailand Market Innovation: Taiwanese Expertise Tailors Solutions Read More »