By James Yang, Executive Assistant to the CEO, Profet AI
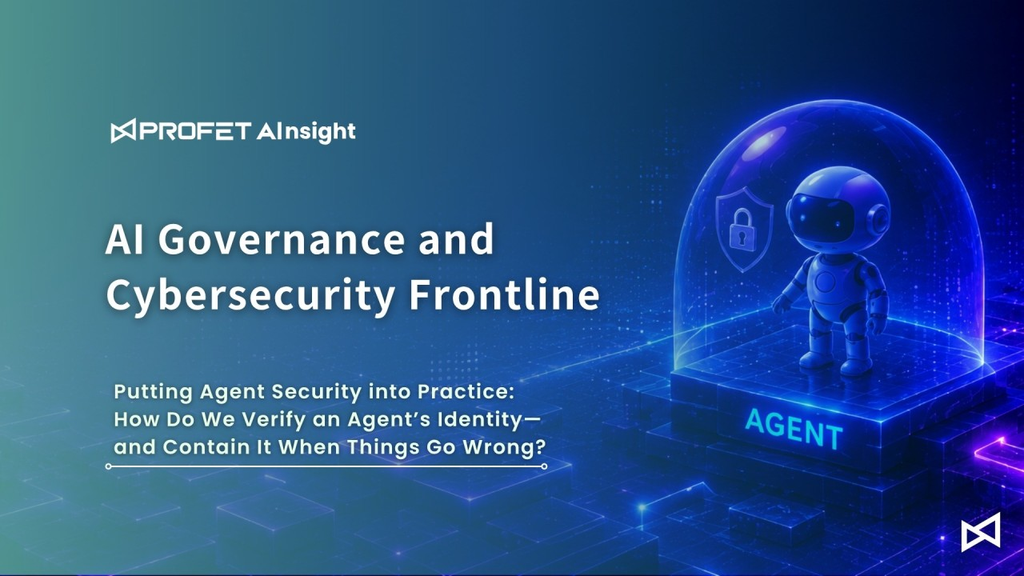
How Taisys, Profet AI, and Zentera illustrate a complete Agentic Zero Trust defense—from hardware-based identity and platform governance to network isolation
In the previous three articles, we explored the threats facing AI Agents, the principles of Zero Trust architecture, and the control processes required to move from security design to enterprise deployment.
Once AI Agents actually enter the enterprise environment, however, a more practical question emerges: How do we turn these security principles into controls that can actually be enforced?
As AI Agents evolve from answering questions to accessing enterprise data, calling MCPs and tools, interacting with backend systems, and even executing tasks with direct business impact, Agent Security is no longer limited to model security. It has become a comprehensive control chain spanning identity, authorization, platform governance, endpoints, and networks.
Architecturally, this defense can be viewed across three distinct layers.
The first asks: Who is actually authorizing this Agent?
The second asks: What is this Agent allowed to do?
The third asks: If the Agent goes out of control, where can it actually reach?
The technologies represented by Taisys, Profet AI, and Zentera map naturally to these three security boundaries.
Taisys dMID: Establishing Trusted Identity with SIM-Based Secure Elements
Traditional enterprise IAM primarily manages the identity of people.
A user authenticates through a username and password, often combined with multi-factor authentication, and is then granted access based on the assigned permissions.
Agentic AI changes this fundamental assumption.When an Agent can continuously act on behalf of a user, enterprises need to verify not only who the user is, but also which Agent is acting, and whether a high-risk operation has actually received human authorization at the moment it matters.
Taisys has extensive experience in SIM, eSIM, and telecommunications identity technologies. One of its key strengths is leveraging the secure hardware embedded within SIM-based technologies to establish a trusted identity foundation.
A SIM card provides characteristics similar to a Secure Element. Sensitive identity credentials and cryptographic keys can be protected within hardware, while cryptographic operations can be performed within the secure environment rather than exposing critical credentials directly to the operating system, browser, or Agent runtime.
This model has been applied for years across telecommunications and financial services. The direction represented by dMID is to extend this established hardware-based trust model toward AI Agent scenarios.
Today, many Agent systems implement Human-in-the-Loop through instructions such as:Before deleting data, making a payment, or modifying a critical setting, ask the user for confirmation.
The problem is that when this rule exists only inside the Agent’s context, the security control remains within the same trust boundary as the Agent’s reasoning.
If the context is compressed, instructions conflict, or the Agent misinterprets the task, the intended approval process may fail.
There have already been notable Agent-related incidents in 2026, including an email Agent deleting large volumes of emails without completing the expected confirmation process, and a coding Agent accidentally deleting production data while troubleshooting an environment issue.
The common factor was not necessarily an external attacker stealing credentials.
Rather, the Agent already had legitimate access—and then used that access incorrectly.
This leads to an important security principle:
Final authorization for high-risk operations should not exist solely inside the Prompt.
A more robust architecture is to allow the Agent to propose an action, while requiring an independent trusted mechanism outside the Agent runtime to re-authenticate the user and verify the authorization before the action is actually executed.
A SIM-based Secure Element can provide a potential Hardware Root of Trust for this model.
In other words: The Agent can determine what needs to be done. It should not be able to prove that the human has approved it.
This separates Human Approval from the Agent’s reasoning process and creates an independent hardware-backed security boundary.
Even if the Agent runtime malfunctions—or is compromised—a high-risk action must still cross a separate trusted authentication boundary before it can be executed.
But verifying who approved an action is only the first step.
Once identity has been established, enterprises must also determine what that user is actually allowed to do through a particular Agent and within a particular context.That is where Agent Governance comes in

Profet AI AI Studio: Building the Policy Control Plane for Agent Governance
In an enterprise Agent architecture, Identity and Authorization must be treated as separate concepts.
Authenticating a user does not mean that the user should be able to access every enterprise resource through every Agent.
Likewise, an Agent with a legitimate identity should not automatically be allowed to access every Knowledge source, Model, MCP, Tool, or enterprise backend system.
This is the core idea behind how Profet AI positions AI Studio as an enterprise AI Agent operation platform.
AI Studio is not simply managing individual Agents. It manages the governance relationships among the different components involved in Agent execution, including Users, Agents, Workflows, Knowledge, Models, AutoML, MCPs, Tools, and Enterprise Systems.
Consider an enterprise FAE Twin.
It may need to search historical technical documents, analyze customer issues, call an AutoML model to analyze manufacturing data, and interact with enterprise systems such as Jira, PLM, or other backend platforms through MCP.
The real governance questions are therefore no longer limited to:
“Can the FAE Twin log in?”
Instead, enterprises need to ask:
- Which customer’s data can it access?
- Which information is read-only?
- Which systems can it modify?
- Which Tool Calls can be executed automatically?
- Which actions require human approval?
These decisions should not be left to the LLM itself.
AI Studio uses mechanisms such as ACLs, Guardrails, Workflows, Knowledge Governance, Tool/MCP Management, and Audit to place enterprise policies outside the Agent’s reasoning process.
The Agent can understand the request, analyze information, and plan a task.
But whether a resource can be accessed, whether a tool can be called, and whether an action requires approval should be determined by an independent policy layer.
A complete Agent control architecture should therefore separate at least three functions:
Reasoning is handled by the Agent.
Policy Enforcement is handled by the governance platform.
Human Approval provides the final authorization for high-risk or irreversible actions.
If all three are embedded in the same Prompt, the Agent effectively becomes the applicant, reviewer, and executor at the same time.
That is fundamentally inconsistent with the principles of Zero Trust.
As AI moves from providing information to taking action, security controls must therefore expand beyond the model layer to cover the entire Agent Execution Chain.
Yet even with trusted identity and platform-level authorization in place, one critical question remains:
What happens if the Agent itself is compromised by Prompt Injection, a malicious MCP, or a third-party tool?
And what happens when an enterprise has Shadow AI that has never been formally registered or governed?
Application-level policies alone may not be enough.Security must extend further down into the infrastructure and network layers.

Zentera Ensage AI: From Shadow AI Visibility to Network Isolation
Zentera Systems has long focused on Zero Trust Network Security. Its CoIP Zero Trust Overlay uses software-defined isolation and micro-segmentation to establish security boundaries around enterprise applications, data, and workloads.
The underlying principle is straightforward:
Even if an attacker compromises one endpoint or obtains valid credentials, they should not automatically be able to move laterally across the enterprise network.
Ensage AI extends this Zero Trust approach to AI Agents.
The collaboration between Profet AI and Zentera brings Agent Governance and underlying Zero Trust network enforcement together.
AI Studio manages the logical authorization relationships between Agents and resources such as Knowledge, Models, MCPs, Tools, and enterprise applications.
Ensage AI extends this control into the Endpoint, Session, and Network layers.
Through zLink, Ensage AI can perform Agent Discovery based on Process Fingerprints and Network Behavior, helping enterprises identify Coding Agents, MCP Servers, and third-party tools based on their actual presence and behavior rather than relying solely on registration.
This addresses the growing challenge of Shadow AI visibility.
At the same time, AI Session Controller provides visibility and control over Prompts, Responses, and Tool Calls, while an intermediary layer can help reduce sensitive credential exposure and limit the potential for compromised credentials to be reused for lateral movement.
Combined with ecosystem risk tracking from Zentera Labs and Virtual Chamber technology, different Agents and workloads can be further isolated within independent network environments.
Consider a simple example.
An Agent working on Project A should not be able to access resources belonging to Project B.
This should not depend solely on a platform policy saying : “Access denied.”
At the network layer, Project B’s services should simply not be reachable by the Agent in the first place.
Likewise, a development Agent compromised through Prompt Injection should not suddenly gain network reachability to a financial system.
A Coding Agent may have permission to interact with a Git repository, but that does not mean it should be able to establish a direct connection to a production database.
This is a critical concept in Zero Trust : Blast Radius Control
Traditional permission design typically starts with the question:
“What permissions does this Agent need to complete its job?”
Zero Trust requires an additional question:
“If this Agent completely loses control one second from now, how much of the enterprise are we willing to let it affect?”
The first question ensures that the Agent can complete its task.
The second determines the maximum potential damage if something goes wrong.
For AI Agents, this distinction is becoming increasingly important. Agents can execute APIs, Commands, and Tool Calls far faster than a human security team can respond. Relying solely on monitoring and alerts after an incident has already occurred may simply be too late.
Therefore, some security controls must exist at an infrastructure layer that the Agent itself cannot bypass.

Three Layers of Agentic Zero Trust: Identity, Governance, and Enforcement
When Taisys, Profet AI, and Zentera are viewed together, it becomes clear that each addresses a different security boundary.
1. Identity & Human Authorization
Taisys dMID uses a SIM-based Secure Element as a hardware trust foundation to protect identity credentials and cryptographic mechanisms, while providing an independent trusted authentication mechanism before critical actions are executed.
The core question this layer answers is:Who actually approved this action?
2. Agent Governance & Policy Control Plane
Profet AI AI Studio governs the access relationships among Users, Agents, Workflows, Knowledge, Models, AutoML, MCPs, Tools, and Enterprise Systems.
Through mechanisms such as ACLs, Guardrails, Workflows, Approval, and Audit, it determines what an Agent is allowed to do within a specific context.
The core question is:What is this Agent allowed to do right now?
3. Compute & Network Enforcement
Zentera Ensage AI extends control from Agent Discovery and Endpoint Visibility to AI Session Control, Micro-segmentation, and Virtual Chamber-based isolation.
It limits the actual network and system environments that an Agent can reach.
The core question is:Even if the Agent is compromised or goes out of control, where can it actually go?
These three security questions are closely related, but they cannot replace one another.
Identity verification cannot by itself prevent a legitimately authorized Agent from moving laterally across the enterprise network.
Platform governance alone cannot guarantee visibility into every unmanaged Shadow Agent running on endpoints.
Network isolation cannot determine whether a high-risk business action has actually received human approval.
A true Agentic Zero Trust architecture therefore requires these three control layers to remain relatively independent while forming a consistent Trust Chain.

Conclusion: From Agent Capability Competition to Agent Trust Architecture
Agentic AI security is unlikely to be solved by a single product.
Agent Identity, Human Approval, Agent Governance, MCP and Tool Management, Endpoint Visibility, Session Control, and Network Isolation represent different areas of expertise.
A more realistic enterprise architecture is therefore not to expect a single Agent platform to recreate every security capability.
Instead, different security layers should each enforce the controls they are best positioned to provide, while connecting through consistent policies, identity, and auditing mechanisms.
Within this architecture :
Taisys provides a Hardware Root of Trust through SIM-based secure hardware.
Profet AI AI Studio serves as the Policy Control Plane for Agent Governance.
Zentera provides Endpoint, Session, and Network Enforcement.
Together, these technologies are not simply three independent products.They can be viewed as components of a broader trust chain spanning identity, authorization, execution, and isolation.For enterprises, this also changes how Agentic AI platforms should be evaluated.
The key questions should no longer be limited to :
- How capable is the model?
- How many Agents can the platform support?
- How many MCPs and tools can it connect?
Instead, enterprises should be asking :
Who initiated the action?
Which Agent executed it?
What policy granted the Agent permission?
Who approved the high-risk action?
Which resources were actually accessed?
And if something goes wrong, can the action be immediately revoked, isolated, and fully traced?
As AI Agents move from information assistants into core enterprise workflows, the focus of security must evolve beyond “preventing the model from giving the wrong answer.”
The real challenge is to ensure that every autonomous action taken by an Agent exists within a trust boundary that is verifiable, authorized, constrained, and auditable.
That is the problem Agentic Zero Trust ultimately needs to solve.